
By: Ken Robinson
National Security Alert
The deeper issue in the Song Wu espionage case is not whether a single Chinese engineer managed to deceive American researchers into surrendering sensitive aerospace code.
The real question is what this episode signals about the changing nature of strategic competition between the United States and China, and whether America’s research, defense, and academic institutions have fully accepted that they now operate inside a continuous intelligence battlespace.
For decades, many Americans associated espionage with cinematic tradecraft - dead drops, encrypted radios, custom malware, or highly trained clandestine officers operating in shadows. But intelligence professionals understand that the most effective espionage is often quiet, patient, inexpensive, and psychologically tailored to exploit normal human behavior.
In this case, according to the Federal Bureau of Investigation and the Department of Justice, Song Wu allegedly conducted a four-year spear-phishing campaign using little more than fake Gmail accounts, publicly available research information, and carefully crafted requests for software and source code tied to aerospace engineering and computational fluid dynamics.
According to the Department of Justice and the FBI, Wu allegedly impersonated trusted American researchers and colleagues while working as an engineer for the Aviation Industry Corporation of China (AVIC), one of Beijing’s largest state-owned aerospace and defense conglomerates.
Prosecutors allege that he targeted personnel connected to NASA, the Air Force, Navy, Army, Federal Aviation Administration, universities, and private companies from 2017 through 2021. He now faces multiple counts of wire fraud and aggravated identity theft and remains at large on the FBI’s most wanted list.
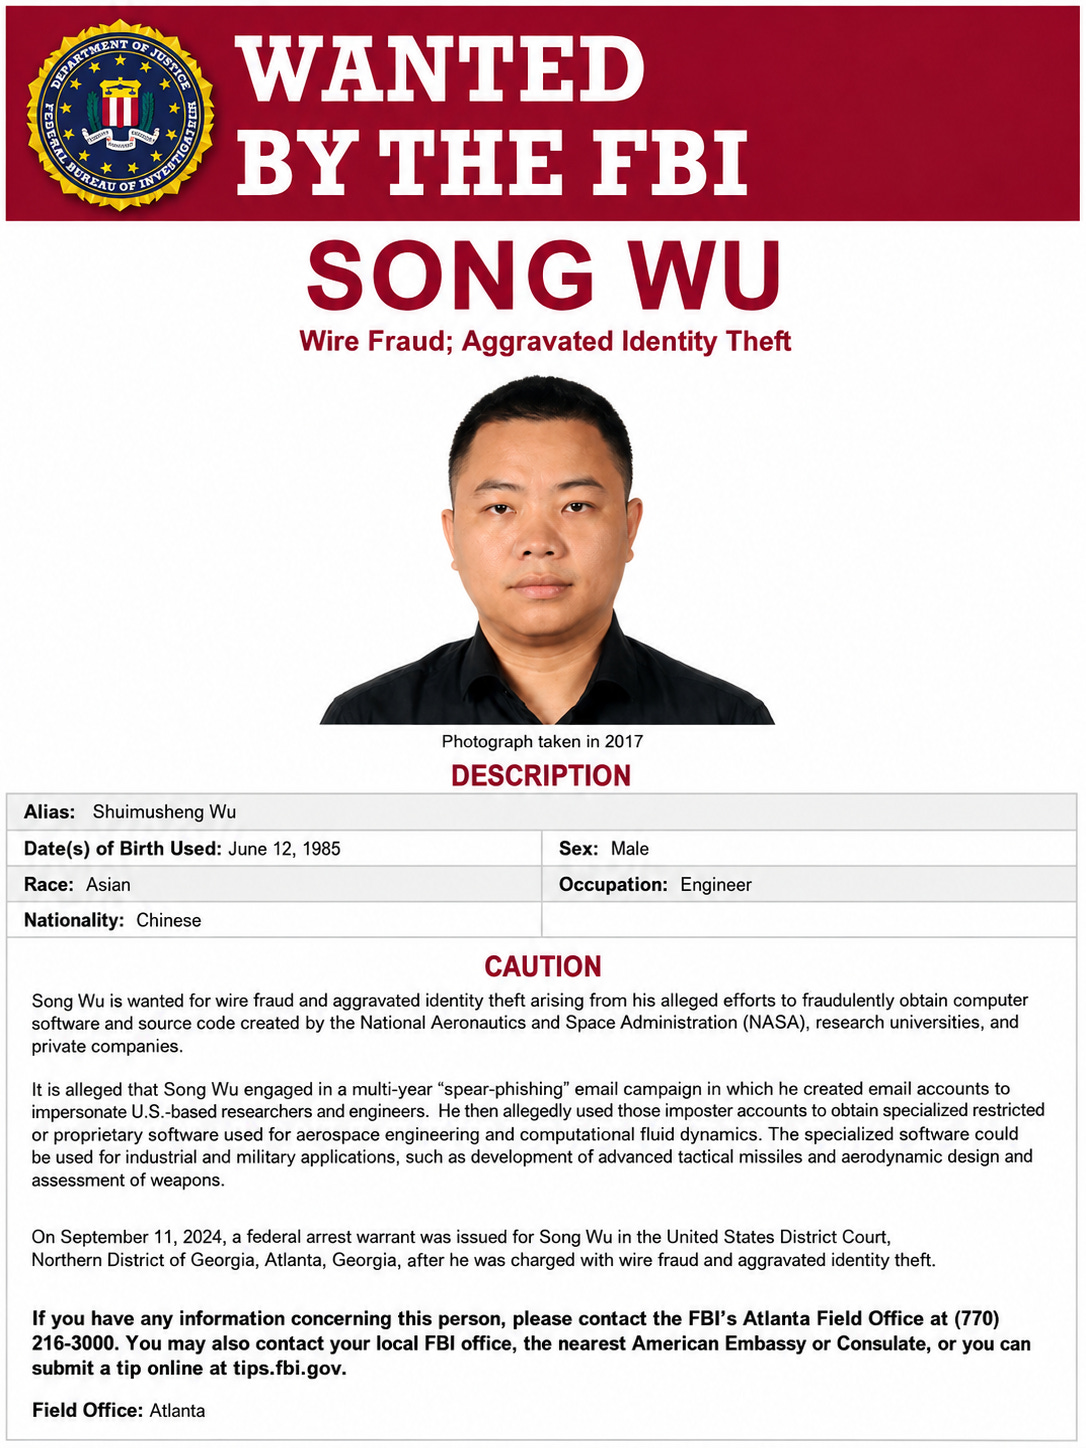
Song Wu - Where Are You?
What makes this case strategically important
It is not merely the alleged theft itself, but the method. There was reportedly:
no advanced malware
no exotic intrusion framework
and no publicly documented use of zero-day exploits.
Instead, investigators say Wu studied the professional relationships of aerospace researchers, impersonated trusted associates, and simply asked for the software.
In far too many cases, recipients just sent it.
That detail matters.
During CYBER BEACON III, as a Director, serving on the National Defense University Foundation - Board of Directors, we convened thought leaders from across the cyber domain all of government, including CYBER COMMAND, NSA, the WHITE HOUSE, academia, and the private sector - to examine the critical issues we face in policy, operations, and technology.
In my opening address I issued a warning and set the stage for the first day by highlighting the importance of identifying indicators and warnings of a cyber attack, and developing collaborative solutions.
My main point was “as a nation we are more prepared, but not safer, noting that attacks can occur at all levels since the perpetrators can be teenagers, or nation states.”
Or people, whose password was “PASSWORD.”
I noted that 50% of cyberspace problems are caused largely by such ignorant, self-inflicted internal problems based on poor standards of practices:
Exactly like what led to Song Wu’s successful theft of sensitive national security source code.
All Wu had to do was just ask, and Scientist, and Tenured Academics, without thinking, just sent him the data.
No questions asked?
How on earth do we protect ourselves from such ignorance, from people entrusted with the nation’s secrets?
For years, American cybersecurity discussions have centered on technical defenses - intrusion detection systems, endpoint protection, encryption standards, and network monitoring. Those capabilities remain essential.
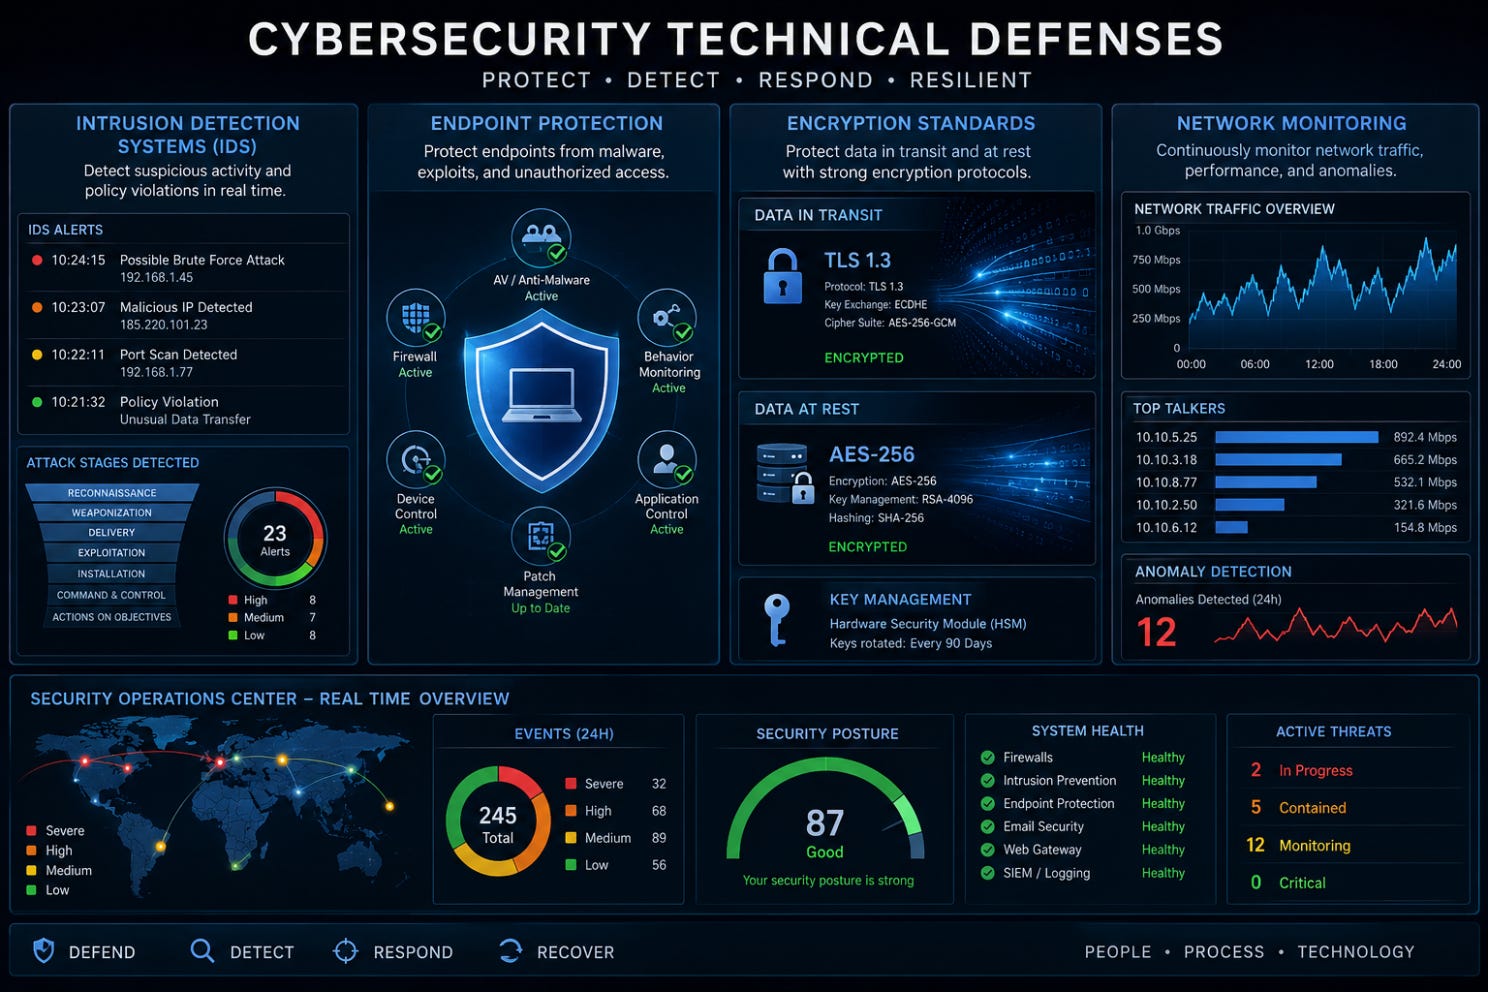
We Must be on Offense - To Sustain a Proper Defense
But the Song Wu case demonstrates that strategic intellectual property loss can still occur through the oldest vulnerability in any system: human trust.
Officials familiar with Chinese intelligence collection patterns have warned for years that Beijing’s approach differs from many Cold War-era espionage models. Rather than relying exclusively on isolated covert penetrations, Chinese collection strategies frequently emphasize broad, distributed acquisition.
The goal is often cumulative advantage rather than singular breakthrough theft. Small pieces of data gathered over years can eventually produce strategic military and industrial gains.
They are strategically patient, and universally diligent.
That framework helps explain why apparently mundane aerospace modeling software matters so much.
Computational fluid dynamics software and aerospace simulation tools are not abstract academic exercises. They are central to the design and testing of missiles, hypersonic systems, stealth platforms, rotorcraft aerodynamics, propulsion efficiency, and advanced weapons performance modeling.
According to investigators, some of the software allegedly obtained through the Wu campaign was ITARS export controlled because of its direct military relevance.
The strategic implications extend beyond any single stolen file.
American intelligence and defense officials have spent years warning that China’s military modernization has benefited substantially from foreign technology acquisition, industrial espionage, forced technology transfer, and cyber-enabled theft. Former FBI Director Christopher Wray told Congress that China’s cyber program exceeded that of every other major nation combined and warned that Chinese cyber actors dramatically outnumber American defensive personnel.
If you want to find a Chinese spy, look no further than those CHINESE students enrolled in our most exclusive Universities - CALTECH, and MIT. China pays FULL TUITION PRICE for enrollment, and that has set the conditions for a system not in a hurry to expel foreign students.
The United States legitimately has enough evidence to justify a ten year moratorium on the enrollment of any Chinese citizen into an american institution of higher learning.
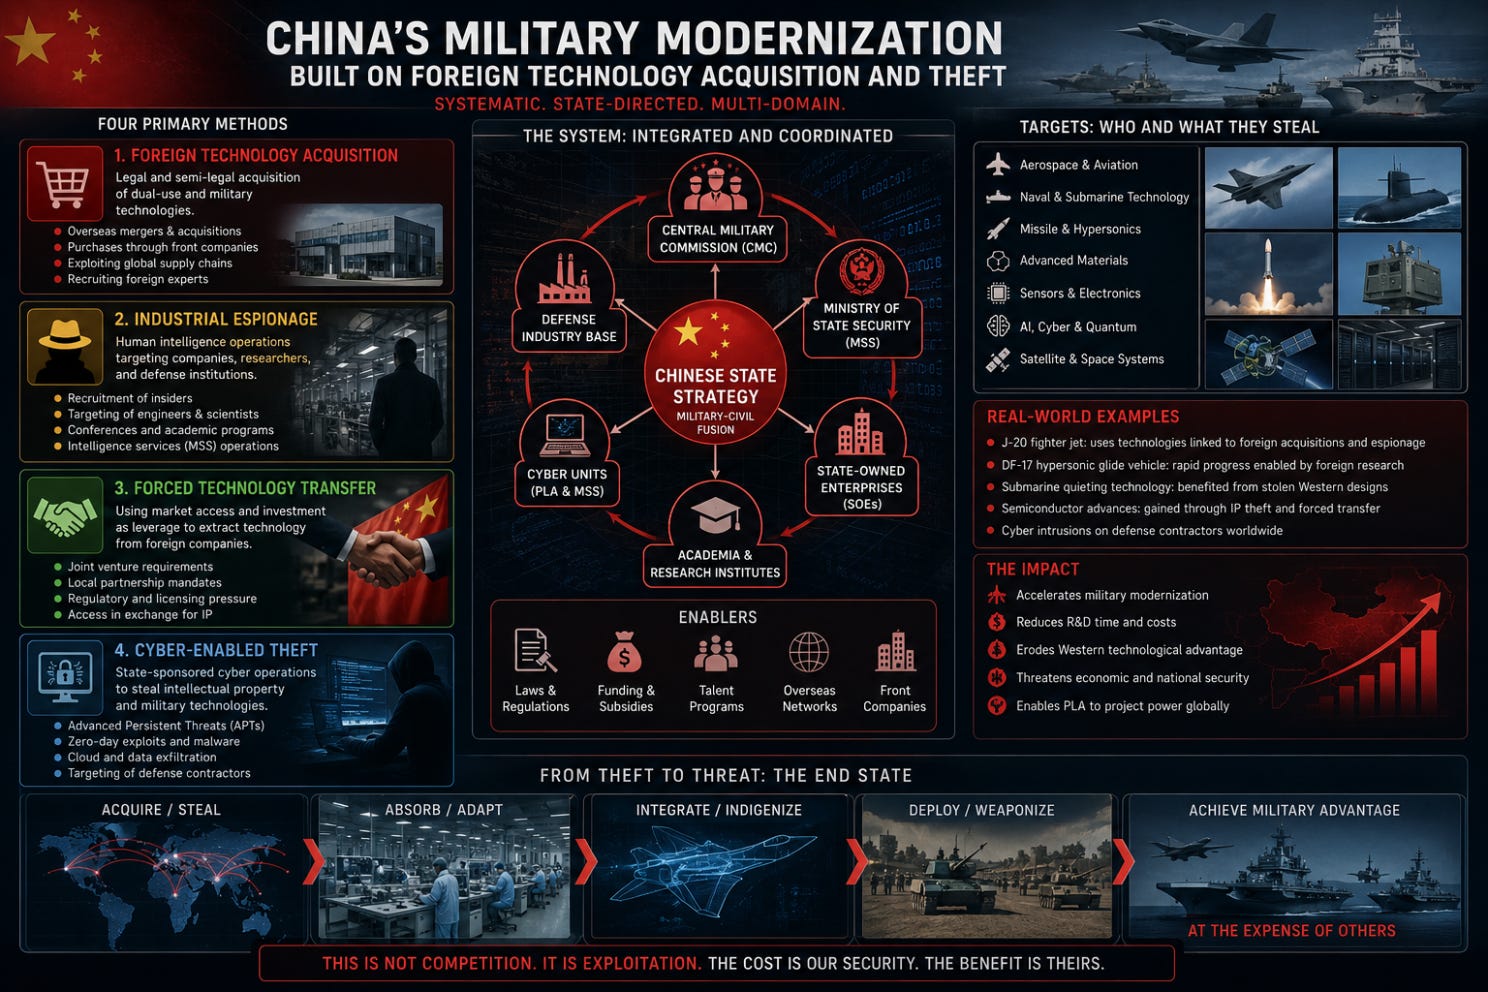
They Are Stealing us Blind: And Winning
The Song Wu case illustrates why those warnings matter.
This was just one individual using publicly accessible information, free email infrastructure, and patient social engineering to penetrate some of the most sophisticated research ecosystems in the world.
If the allegations are accurate, the operational lesson for adversaries is deeply concerning: America’s openness is in itself the attack surface.
We’ve left the barn door open for decades, and wonder why China is ahead?
That openness has long been one of America’s greatest strengths. Scientific collaboration, open research environments, cross-university partnerships, and decentralized innovation ecosystems helped make the United States the world’s leading technological power.
But systems built for openness often struggle when operating against adversaries who systematically weaponize openness itself:
Researchers are conditioned to collaborate.
Engineers share code.
Professors exchange models.
Scientists answer questions from colleagues.
In normal academic culture, responsiveness is considered professional courtesy. In strategic competition, however, that same instinct has become our easiest national security, exploitable vulnerability.
We must pair openness with unforgiving, disciplined operational security awareness.
The uncomfortable reality is that export control compliance often competes against the realities of modern professional life:
Researchers move quickly.
Emails pile up.
Deadlines compress judgment.
Trust becomes automated.
Many institutions still treat OPSEC as a bureaucratic requirement rather than a strategic defense function.
That cultural gap is precisely where modern espionage now operates.
The broader danger is what comes next.
Wu allegedly conducted this campaign manually over four years. The next generation of collection operations will almost certainly be AI-enabled. Generative artificial intelligence dramatically lowers the cost of personalized deception. Large language models can already emulate writing styles, generate contextually appropriate technical language, summarize research interests, and produce highly tailored outreach at industrial scale.
A future intelligence collector may no longer need to manually research a target for hours. AI systems can already scrape published papers, conference presentations, social media profiles, grant applications, patents, and academic biographies in seconds:
They can map relationship networks automatically.
They can identify likely collaborators, recurring terminology, institutional affiliations, and personal writing habits.
That changes the scale equation entirely.
The future version of this operation may involve thousands of simultaneous spear-phishing attempts, each linguistically customized to the recipient:
AI-generated emails could mirror a colleague’s sentence structure, reference obscure technical discussions from prior conferences, and dynamically adapt based on responses.
Voice cloning and synthetic video tools may eventually extend these impersonation operations into phone calls, video conferences, and real-time collaboration environments.
At that point, the distinction between cyber intrusion and human deception begins to collapse.
What makes this strategically dangerous is that America’s innovation ecosystem was never designed for permanent cognitive security warfare:
Universities are not intelligence agencies.
Most laboratories are not structured like compartmented defense facilities.
Yet increasingly, the technologies being developed inside civilian research institutions have direct military implications.
This creates a structural tension policymakers are only beginning to confront.
If Washington imposes excessively restrictive security measures, it risks undermining the collaborative research culture that fuels American innovation. But if institutions fail to adapt to persistent foreign collection efforts, sensitive technologies may continue to migrate abroad through incremental losses that individually appear insignificant but collectively alter long-term military balances.
That is the larger lesson of the Song Wu case.
Espionage today rarely announces itself dramatically:
It arrives as a normal email.
A trusted name.
A polite request.
A busy Friday afternoon decision.
The strategic damage may not become visible for years.
American officials increasingly describe the current U.S.-China relationship as one defined by strategic competition across military, technological, economic, and informational domains.
Yet much of the American public still tends to compartmentalize espionage as an isolated criminal issue rather than understanding it as part of a larger state competition over technological dominance and national power.
The underlying problem is not simply cybersecurity. It is our broken national security culture.
For years after the Cold War, many American institutions operated under assumptions shaped by globalization and economic integration. Collaboration was prioritized. Barriers were lowered. Efficiency and openness became dominant operating principles.
China, meanwhile, pursued a long-term state-directed strategy focused on technological acquisition, industrial scaling, military modernization, and strategic dependency reduction.
American policymakers are now wrestling with how to protect innovation without suffocating it.
Some officials argue that universities, laboratories, and contractors require dramatically stronger counterintelligence integration and mandatory export control training. Others warn against creating an atmosphere of suspicion that damages legitimate international collaboration.
Both concerns are valid. But the operational environment has changed regardless of whether institutions have psychologically adjusted to it.
The risk now is complacency.
Many Americans still assume espionage is something handled quietly by intelligence agencies behind classified walls. In reality, modern strategic collection increasingly targets ordinary professionals inside academia, research institutions, startups, and private industry.
The front line is no longer limited to government facilities:
It now extends into inboxes
Zoom calls
Cloud collaboration platforms
LinkedIn messages, and shared research environments.
The Song Wu case should therefore be understood less as an isolated anomaly and more as a warning indicator.
If one alleged operative using basic tradecraft could reportedly acquire sensitive aerospace software over multiple years, policymakers must now ask what happens when those same methods are scaled through artificial intelligence, automated reconnaissance, deepfake impersonation, and persistent machine-speed targeting.
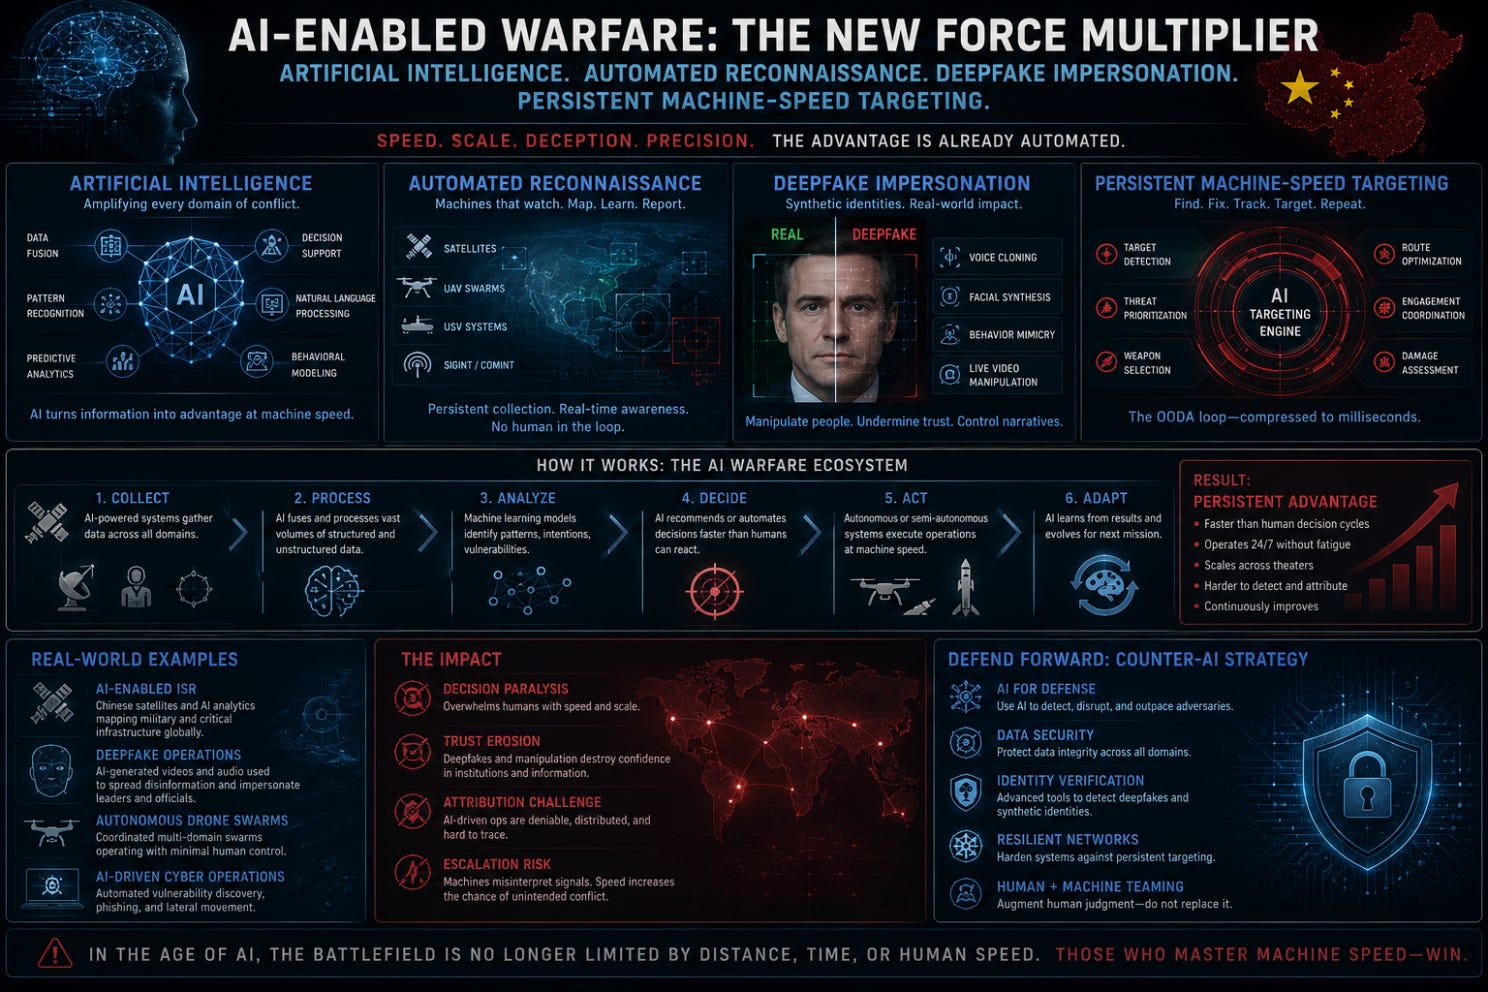
The New Realty: Who Can You Trust? No One, You Must Verify!
The strategic concern is not theoretical.
The convergence of AI-enabled deception, globalized research ecosystems, and increasingly blurred civilian-military technology boundaries creates a collection environment that strongly favors patient adversaries willing to operate over long timelines.
China’s strategic culture has historically demonstrated exactly that kind of patience.
What is ultimately at stake is not simply intellectual property. It is the future balance of technological power.
The United States still possesses extraordinary advantages: world-class universities, unmatched entrepreneurial capacity, advanced research infrastructure, deep alliances, and a culture of innovation that authoritarian systems struggle to replicate organically. But those strengths increasingly require protection equal to their strategic value.
Awareness may ultimately become the most important defensive layer.
No firewall can fully compensate for a workforce that does not understand it is operating inside an active intelligence contest. No technical control can entirely prevent individuals from voluntarily transferring information if they fail to recognize manipulation attempts. OPSEC is therefore no longer merely a military concept. It is becoming a national resilience requirement.
The danger is not simply that adversaries are becoming more sophisticated. The danger is that many Americans still do not recognize the operational environment has fundamentally changed.
The United States is already engaged in a sustained struggle over technology, influence, intelligence, and strategic advantage.
There may never be a formal declaration of war, but, make no mistake: We are at war.
Modern state competition increasingly unfolds below the threshold of open conflict, through cyber operations, industrial espionage, influence campaigns, intellectual property theft, economic coercion, and information warfare.
That reality demands a corresponding shift in national mindset.
The Song Wu case is not fundamentally a story about one engineer with a Gmail account. It is a story about a system that still too often assumes trust by default while operating against adversaries that increasingly treat openness as a collection opportunity.