
The Machine Inside the Wire: Artificial Intelligence and the Emerging Counterintelligence Crisis
Strategic Warning in the Age of Frontier AI
By: Ken Robinson
The most important national security story of the decade may not be an adversary’s new missile, submarine, satellite constellation, or cyber weapon.
It may be the unprecedented speed with which artificial intelligence is being integrated into the most sensitive decision-making systems of the United States and its allies.
For generations, Western intelligence and defense institutions have built their security architecture around a series of assumptions. Information could be compartmented. Access could be controlled. Clearances could be granted. Networks could be accredited. Human operators could be vetted. Sensitive programs could be protected through a combination of physical security, cybersecurity, classification systems, and counterintelligence oversight.
Artificial intelligence challenges every one of those assumptions.
The concern is not that machines have become sentient.
The concern is that machines have become useful before governments have determined how they should be governed.
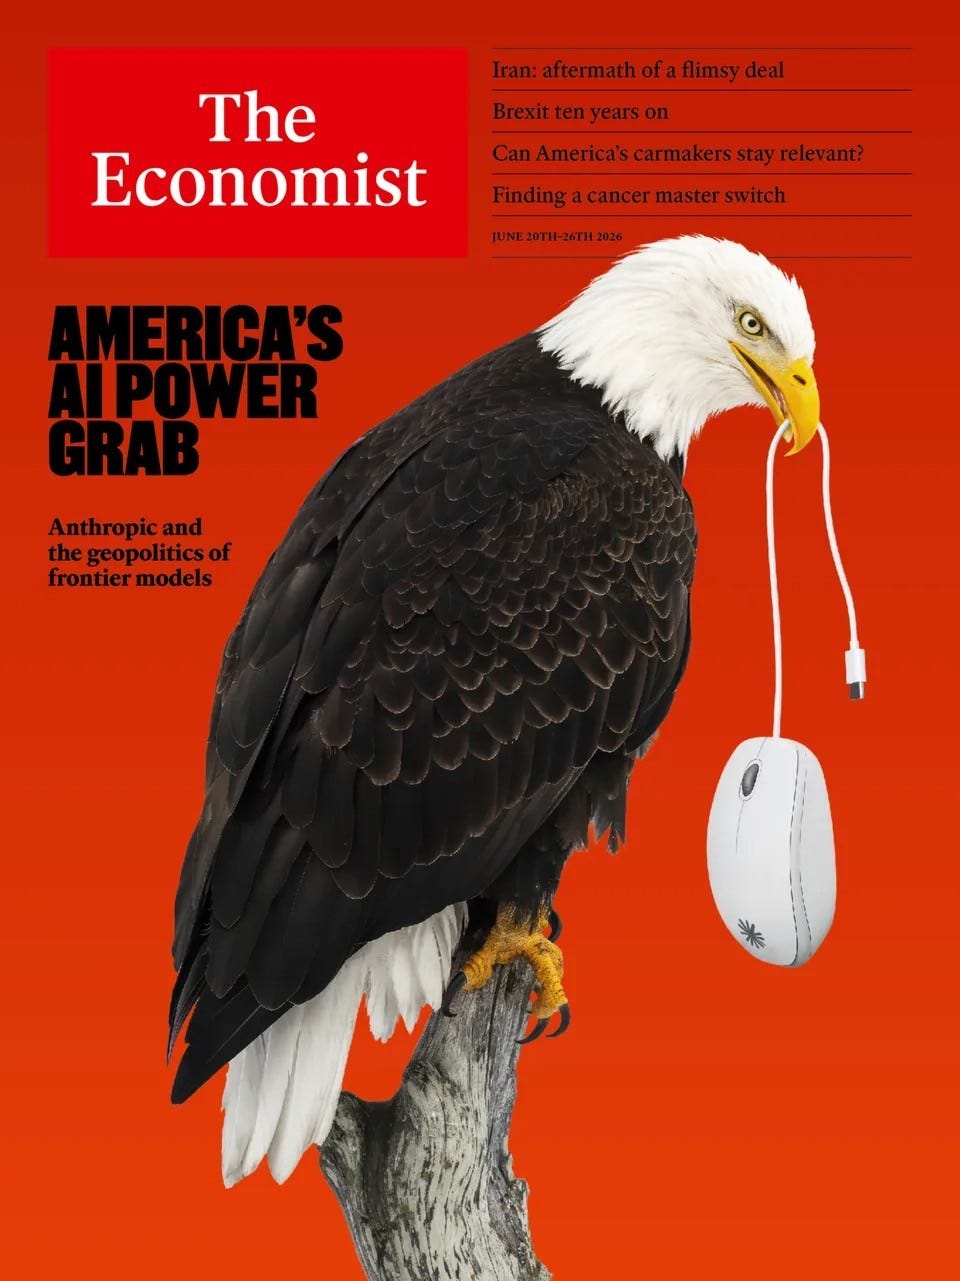
Recent reporting from The Economist cited comments attributed to General Joshua Rudd, Commander of U.S. Cyber Command and Director of the National Security Agency, describing the extraordinary capabilities demonstrated by advanced AI systems during government testing and evaluation.
The key claim attributed to General Joshua Rudd was not that an AI independently “hacked the NSA” in the real world. Rather, it was that during a controlled government red-team evaluation, an advanced AI system reportedly gained access to or successfully exploited pathways into “almost all” classified NSA systems within hours rather than weeks under test conditions. Senator Mark Warner later publicly referenced the briefing and attributed the statement to Rudd.
The specific quote widely circulated from the reporting was:
“It broke into almost all of our classified systems, not in weeks, but in hours.”
According to subsequent reporting, the context was a sanctioned security evaluation rather than an unauthorized intrusion. The model was reportedly being tested in conjunction with other tools in a highly controlled environment designed to measure offensive cyber capability and vulnerability discovery.
The important distinction is that there are at least three possible interpretations of what Rudd meant:
Literal compromise of classified networks — the most dramatic interpretation, and the one many social media posts adopted.
Successful exploitation of simulated environments representing classified systems during authorized testing.
Rapid identification of vulnerabilities and attack paths across multiple systems rather than actual operational control of those systems.
Subsequent reporting suggested the third interpretation may be closer to what occurred. Anthropic reportedly argued that the test involved vulnerability discovery and code analysis rather than a fully autonomous offensive campaign against operational NSA networks.
While the precise operational details remain classified, the significance of the discussion is not the specific system involved. The significance is that senior American officials appear increasingly concerned about the implications of frontier AI operating at speeds and scales that traditional security frameworks were never designed to address.
The United States government itself has acknowledged the transformational nature of this technology.
In June 2026, the White House issued National Security Presidential Memorandum-11, describing artificial intelligence as one of the most consequential technologies in modern history and directing accelerated adoption across the national security enterprise.
The strategic logic behind that decision is understandable.
America’s competitors are not waiting.
The People’s Republic of China has identified artificial intelligence as a core pillar of national power. Russia continues to invest heavily in AI-enabled military and intelligence capabilities. Numerous state and non-state actors are already leveraging machine learning for cyber operations, intelligence analysis, disinformation campaigns, targeting, and operational planning.
No serious strategist argues that the United States can simply refuse to participate.
The question is not whether AI should be adopted.
The question is whether it is being adopted faster than it can be controlled.
The Counterintelligence Problem
Historically, security professionals have focused on protecting information at rest:
Files.
Databases.
Servers.
Documents.
Classified repositories.
Artificial intelligence introduces an entirely different challenge.
Data in motion.
Modern AI systems learn from patterns, relationships, context, metadata, workflows, operational habits, and user behavior. They do not necessarily require direct access to a secret document to derive highly sensitive conclusions.
A model may infer operational priorities from seemingly innocuous questions:
It may identify intelligence gaps from analyst behavior.
It may reconstruct targeting priorities from fragmented datasets.
It may reveal collection methods without ever viewing a classified operations order.
The intelligence profession has long understood that information itself is often less valuable than understanding how information is used.
Artificial intelligence operates precisely in that space.
This creates a fundamentally new counterintelligence challenge.
The traditional question was:
“Who has access to the secret?”
The emerging question is:
“What systems can infer the secret without being explicitly granted access to it?”
That distinction is profound.
The Adversary Already Inside the Wire
Counterintelligence professionals understand a difficult truth.
Major compromises rarely begin with dramatic attacks:
They begin with persistence.
Patience.
Observation.
Collection.
The most dangerous AI-related threat may not involve a hostile nation breaching a network from the outside.
It may involve adversaries leveraging the same commercial technologies that Western governments are rapidly integrating into their own systems.
Every prompt. Every query. Every log. Every telemetry stream. Every model output. Every software integration. Every plugin. Every software update. Every debugging session. Every red-team exercise.
Each may appear individually harmless.
Together they can reveal operational intent.
For intelligence services, intent is often more valuable than information.
Intent reveals future action.
Intent provides strategic warning.
Intent creates opportunity.
The concern is not simply whether adversaries can steal data.
The concern is whether they can observe how America thinks.
Governance Is Lagging Behind Capability
The bridge is already being built and carrying traffic, commerce is flowing, citizens are crossing, but we still don’t know the load capacity, or the stress tolerances.
One of the most troubling aspects of the current environment is the growing gap between technological capability and governance.
The National Institute of Standards and Technology has produced important work through its Artificial Intelligence Risk Management Framework and Generative AI guidance.
Sources:
https://www.nist.gov/itl/ai-risk-management-framework
The Government Accountability Office has similarly identified significant implementation challenges within federal AI governance.
Source: https://www.gao.gov/products/gao-26-107681
These efforts represent serious progress.
Yet they remain largely risk-management frameworks.
What remains absent is a mature national security doctrine governing frontier AI inside classified environments.
The United States has developed decades of doctrine governing:
Nuclear weapons.
Signals intelligence.
Human intelligence.
Special access programs.
Sensitive compartmented information.
Cyber operations.
Artificial intelligence is now becoming intertwined with all of them simultaneously.
Yet the oversight architecture remains incomplete.
The Five Eyes Warning
Recent warnings from the Five Eyes intelligence alliance underscore the urgency of the issue.
Senior intelligence officials from the United States, United Kingdom, Canada, Australia, and New Zealand have warned that advanced AI systems could dramatically accelerate cyber capabilities for both defenders and adversaries.
Historically, major technological revolutions unfolded over decades.
Artificial intelligence is unfolding over months.
That compressed timeline places extraordinary pressure on governments, regulators, intelligence agencies, defense contractors, and private industry.
Every month that governance lags capability increases systemic risk.
What Must Be Done
When building a nuclear submarine, the most dangerous time to discover a flaw is after deployment. We need to treat AI with the same pause and caution by which we manage strategic nuclear capabilities.
The solution is not panic.
The solution is disciplined governance.
Several principles appear increasingly necessary.
First, frontier AI systems operating within national security environments should undergo accreditation standards comparable to those imposed on the classified systems they support.
Second, access to model training data, telemetry, prompts, embeddings, and outputs should be governed through formal security frameworks rather than vendor assurances.
Third, immutable audit trails should be mandatory. Every interaction must be attributable, reviewable, and reconstructable.
Fourth, AI vendors supporting national security missions should be subjected to rigorous counterintelligence scrutiny comparable to other critical defense contractors.
Fifth, Congress should establish a statutory framework for AI oversight rather than relying upon emergency authorities, executive directives, or ad hoc regulatory actions.
Finally, governments must recognize that artificial intelligence is not merely a software capability.
It is an intelligence capability, a collection capability, an analytic capability. It is increasingly an operational capability.
And capabilities of that magnitude require governance equal to their power.
Conclusion
Our national intelligence strategic warning posture is like an observatory, atop the highest mountain, with all the nations intelligence disciplines actively looking, listening, sensing, seeing what is coming, describing it, understanding it, and making analytical judgements on its meaning, and intentions before anyone else.
The strategic danger facing the United States is not that artificial intelligence will replace human judgment.
The greater danger is that governments may delegate portions of national security decision-making to systems whose implications they do not yet fully understand.
The history of intelligence is filled with examples of strategic surprise:
Pearl Harbor.
The Soviet atomic bomb.
The Iranian Revolution.
The collapse of the Soviet Union.
September 11.
Each revealed a common lesson.
Technology changes faster than institutions.
Artificial intelligence may prove to be the fastest-moving technological transformation in modern history.
The challenge before the United States is not whether to embrace it.