
Preparing to Go It Alone?
By: Ken Robinson
Key Judgments
The central strategic question confronting the West is not whether NATO can defeat Russia in a conventional war. It is whether NATO can adapt—fast enough—to a form of conflict Russia is already executing continuously below the threshold of declared war.
Minus the United States?
Russia is not “preparing for hybrid warfare”. It is already prosecuting it.
The alliance is not failing. It is transforming—but at a pace constrained by political consensus, bureaucratic friction, and uneven assessments of American strategic reliability.
The outcome of this competition will not be decided in a single battle or campaign. It will be determined by tempo, cohesion, and the sustained will to adapt under pressure, and go it alone.
The NATO Summit
The upcoming summit of NATO is formally scheduled for July 7–8, 2026, and will take place in Ankara, Turkey, specifically at the Beştepe Presidential Compound (Cumhurbaşkanlığı Külliyesi)—the Turkish presidential complex that will host heads of state and government.
This location and timing place the alliance’s leadership at the political center of Turkey during a period of heightened strategic uncertainty, reinforcing the summit’s importance as a decisive moment for NATO’s future direction.
As NATO prepares to convene, allied governments are entering the meeting under an unusual cloud of strategic uncertainty: the renewed possibility that the United States could scale back or in extremis, withdraw from the alliance altogether.
This prospect cuts to the core of NATO’s deterrence model, which has been anchored for over seven decades by U.S. military power, nuclear guarantees, and command-and-control infrastructure.
European members are now quietly assessing worst-case contingencies, including independent force projection, accelerated defense spending, and alternative security architectures, should Washington’s political trajectory continue to question alliance commitments.
At the same time, frontline states-particularly those bordering Russia-are pressing for clarity, concerned that ambiguity in U.S. intent could invite miscalculation in Moscow.
The summit in Turkey is therefore not just another diplomatic gathering; it is shaping into a stress test of NATO’s cohesion, credibility, and long-term viability in an era where the alliance’s foundational assumption—reliable American leadership—can no longer be taken as guaranteed.
Strategic Framing: The Inflection Point
The Russian Federation - State Power
The present moment has been shaped by a convergence of operational pressure from Moscow and political recalibration across Europe that has unfolded steadily since Russia’s 2022 invasion of Ukraine and accelerated through 2025–2026.
Russian intelligence and military services are actively conducting operations across the European theater—from the Baltic states to Germany, from Poland to the United Kingdom—while European governments are simultaneously planning for the worst case scenario.
This dynamic has forced national leaders, defense ministries, and intelligence services to rethink not just how they would respond to war, but how they survive sustained pressure short of it.
The problem is not theoretical.
It is unfolding in real time across infrastructure, elections, financial systems, and public trust. The emerging response is structural: layered defense, redundancy, and parallel mechanisms designed to prevent paralysis if a single guarantee fails.
The Russian Intelligence System: Structure and Function
The Russian intelligence apparatus, directed from Moscow under the authority of the Kremlin and President Vladimir Putin, operates as a unified instrument of state power rather than a set of independent agencies.
Since the early 2000s, this system has been rebuilt to serve regime security, foreign influence, and military advantage simultaneously.
Its three principal services:
The Federal Security Service - FSB
FSB
The Federal Security Service is the primary domestic security and counterintelligence service, the closest institutional descendant of the KGB’s internal arm.
Leadership (widely reported): Director Alexander Bortnikov
Primary Mission: Regime security, internal stability, counterintelligence, counterterrorism, border security
Primary Western Target: Western intelligence penetration efforts inside Russia, foreign NGOs, diplomatic networks, and any perceived internal influence linked to the West.
The FSB’s center of gravity is internal control, but its reach extends outward in what Moscow defines as “defensive” operations. It monitors foreign diplomats, disrupts suspected Western recruitment efforts, and increasingly conducts cyber and influence operations with external impact. It is also heavily involved in Ukraine, particularly in pre-war political preparation and occupation governance - where its failures in assessing Ukrainian resistance were significant.
Foreign Intelligence Service - SVR
SVR
The SVR is Russia’s external intelligence service, responsible for classic espionage abroad.
Leadership (widely reported): Director Sergey Naryshkin
Primary Mission: Strategic intelligence collection, political influence, recruitment of foreign assets
Primary Western Target: U.S. government institutions, NATO leadership, European political systems, think tanks, and economic centers of gravity.
The SVR is the closest analog to the CIA’s Directorate of Operations. It runs long-term espionage campaigns, including the “illegals” program - deep-cover operatives embedded for decades. Its tradecraft emphasizes patience, relationship-building, and strategic access rather than rapid operational tempo.
But the SVR operates within a politicized system. Its reporting is often shaped by what leadership wants to hear. That creates risks.
When strategic assessments are wrong, they are wrong at scale: Russia’s Three Day Special Military Operation?
Main Directorate of the General Staff - GRU
GRU
The GRU is Russia’s military intelligence service, and in many ways the most aggressive and operationally active.
Leadership (widely reported): Chief Igor Kostyukov
Primary Mission: Military intelligence, battlefield support, covert action, sabotage, cyber operations.
Primary Western Target: NATO military infrastructure, logistics networks, defense industries, and critical infrastructure across Europe.
Unlike the SVR, the GRU is not patient by design. It is action-oriented.
Its operational arms include:
GRU Special Forces (Spetsnaz GRU): Elite military units trained for reconnaissance, direct action, sabotage, and unconventional warfare. These forces have been heavily deployed in Ukraine, both in the initial invasion phase and in ongoing operations behind the lines.
Unit 29155: A covert action and sabotage unit linked to assassination attempts, destabilization operations, and clandestine attacks across Europe.
Unit 26165 and Unit 74455: Cyber warfare units associated with major hacking campaigns, including election interference and infrastructure targeting.
The GRU’s strength is its willingness to act. Its weakness is that action often comes at the cost of discipline. A number of exposed operations in Europe - from poisoning attempts to cyber intrusions - have revealed patterns of sloppiness under pressure.
These agencies divide responsibilities on paper but overlap in practice, operating across Europe, Ukraine, and global economic centers.
Their activities include:
recruiting agents inside Western institutions
penetrating defense industries
conducting sabotage missions
and shaping political narratives abroad.
The system is designed to collect intelligence and act on it, often within the same operational cycle, compressing the time between awareness and action in ways Western bureaucracies struggle to match.
Russian Operational Doctrine: Hybrid Warfare as Default
Russian strategy has evolved over the past decade into a continuous campaign that blends military and non-military tools across multiple domains.
Two Key Players Have Been:
Russian Spetsnaz
Spetsnaz
“Spetsnaz” is not a single organization but a category of special purpose forces across multiple services, most prominently within the GRU.
Primary Mission: Direct action, reconnaissance, sabotage, unconventional warfare.
Primary Western Target: NATO forward positions, supply lines, critical infrastructure, and high-value targets in contested environments.
In Ukraine, Spetsnaz units were tasked with decapitation strikes, reconnaissance of key infrastructure, and support to airborne and mechanized forces. Early failures in Kyiv highlighted both their capability and their vulnerability when operating without accurate intelligence.
WAGNER GROUP (Now Absorbed & Redistributed)
Wagner Group
The Wagner Group emerged as a deniable paramilitary force operating in the gray space between state and non-state actor.
Founder (historically): Yevgeny Prigozhin
Operational Role: Proxy warfare, expeditionary combat, regime support abroad.
Primary Theaters: Syria, Libya, Central African Republic, Mali, and Ukraine.
Wagner’s rise was driven by utility. It allowed the Kremlin to project force without formal attribution. In Ukraine, Wagner played a significant role in the early and mid-phases of the war, particularly in high-casualty operations like Bakhmut. They were used as shock troops, often with brutal tactics and minimal regard for losses.
But Wagner’s strength - autonomy - became its fatal flaw.
Prigozhin’s challenge to the Russian military leadership in 2023 exposed the limits of deniable power structures. The subsequent dismantling of Wagner was swift. Its leadership was eliminated or neutralized, and its global network was absorbed into the Russian state security apparatus - primarily under the Ministry of Defense and GRU-linked structures.
Today, Wagner does not exist as it once did. Its functions remain. They have simply been redistributed across state-controlled entities, continuing Russia’s proxy warfare model under tighter control.
This approach, visible in Ukraine since 2014 and expanded across Europe after 2022, relies on cyber intrusions into infrastructure, coordinated disinformation campaigns targeting democratic institutions, sabotage of logistics networks, and the use of criminal intermediaries to maintain plausible deniability.
These activities are conducted daily, often below the level that would trigger a formal military response, but cumulatively they degrade cohesion and increase uncertainty among NATO members.
The intent is not to win a decisive battle in a single moment, but to create friction everywhere—slowing decision-making, raising political costs, and forcing adversaries to expend resources defending against a thousand small disruptions rather than one large attack.
Russian Strengths and Vulnerabilities
Russia’s intelligence services bring a set of enduring advantages shaped by decades of centralized control and operational continuity. They can sustain long-term operations, accept higher levels of risk, and integrate intelligence directly into national strategy without the same political constraints faced by democracies.
However, these strengths are offset by systemic weaknesses that have become increasingly visible since 2022. Intelligence reporting is often influenced by leadership expectations, creating blind spots at the highest levels. Internal rivalries between services degrade coordination.
Russian intelligence understands the United States and NATO in broad psychological terms. They study our systems, our politics, and our fractures. They are less interested in declared policy than in behavioral patterns under stress.
They know our strengths: economic power, alliances, technological superiority. But they focus on perceived weaknesses: political division, legal constraints, and what they assess as fluctuating strategic will.
Where they are often overestimated is in precision. Their analysis is filtered through a system that rewards alignment with leadership expectations. That distortion has been evident in Ukraine.
They understand us broadly. They do not always understand us correctly.
Corruption distorts reporting accuracy. And most critically, Russian operatives now face a Western environment saturated with data—financial, digital, and biometric—that exposes their activities at a scale not present during the Cold War.
The result is a system that remains dangerous but is increasingly detectable and, at times, strategically miscalibrated.
The Surveillance Environment They Struggle With
Russia operates effectively in controlled environments. It struggles in open, technologically saturated ones.
Western societies are not less surveilled. They are differently surveilled. Data is decentralized, aggregated, and analyzed across public and private systems. This creates a detection environment that is difficult to map and harder to evade.
Russian officers operating abroad face constraints they do not encounter at home. Their tradecraft, while historically strong, has not fully adapted to this reality. That is why repeated networks have been exposed across Europe.
The Surveillance Battlespace
NATO
The modern operational environment across North America and Europe has been transformed by the explosion of data generated through daily life.
Every financial transaction, airline ticket, mobile device signal, and online interaction contributes to a layered surveillance ecosystem spanning government databases and private sector platforms.
Intelligence and law enforcement agencies now operate within this dense information space, allowing them to track movements, identify patterns, and correlate behaviors at unprecedented speed.
For Russian operatives attempting to conduct covert activity inside these societies, the challenge is no longer simply avoiding human detection—it is navigating a system where anonymity is increasingly rare.
This has shifted the balance: espionage is still possible, but exposure is far more likely, and once detected, networks can be rapidly mapped and dismantled.
Hybrid Warfare: Their Center of Gravity
Russian intelligence excels in the gray zone.
Cyber operations, disinformation, political influence, economic pressure, and sabotage are integrated into a unified strategy designed to create confusion and delay decision-making.
In Europe, this includes election interference, support to extremist movements, and targeted disruption operations. In Ukraine, it includes cyber attacks, intelligence-driven targeting, and influence campaigns aimed at Western audiences.
The objective is not always victory.
It is paralysis.
Strengths and Weaknesses
Strengths:
Strategic patience (SVR illegals program)
Integration with state power (FSB regime security)
Operational aggression (GRU covert action)
Mastery of gray-zone conflict
Weaknesses:
Politicized intelligence
Inter-service rivalry (FSB vs GRU vs SVR)
Tradecraft gaps in high-surveillance environments
Overreliance on coercive recruitment
Exposure of operations due to operational sloppiness
Ukraine: The Active Intelligence War
Ukraine has become the central arena where these competing intelligence systems are being tested under wartime conditions.
Since Russia’s full-scale invasion in February 2022, its intelligence services have operated inside Ukraine to support military targeting, manage occupation zones, and influence both local populations and Western audiences.
Drone Killing Tanks:
On the battlefields of Ukraine, a fundamental shift in warfare is underway—where low-cost, intelligence-driven drone operations are systematically dismantling high-value armored platforms.
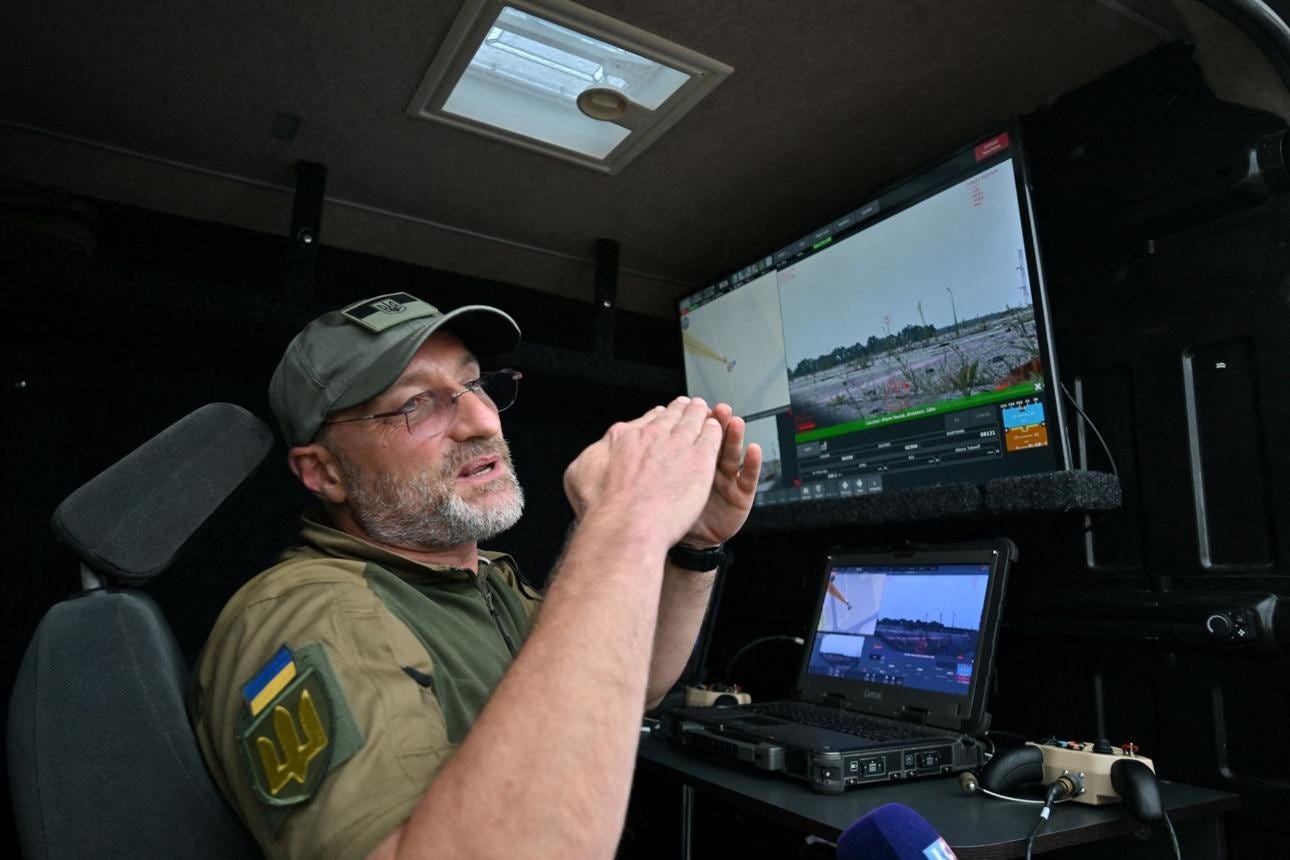
Small, commercially derived first-person-view (FPV) drones, guided in real time by operators linked to distributed intelligence networks, are striking tanks, artillery, and logistics vehicles with precision once reserved for advanced missile systems. This is not simply a technological evolution; it is a doctrinal transformation in which intelligence, surveillance, and reconnaissance are fused directly into the kill chain, compressing the time between detection and destruction to minutes—or seconds.
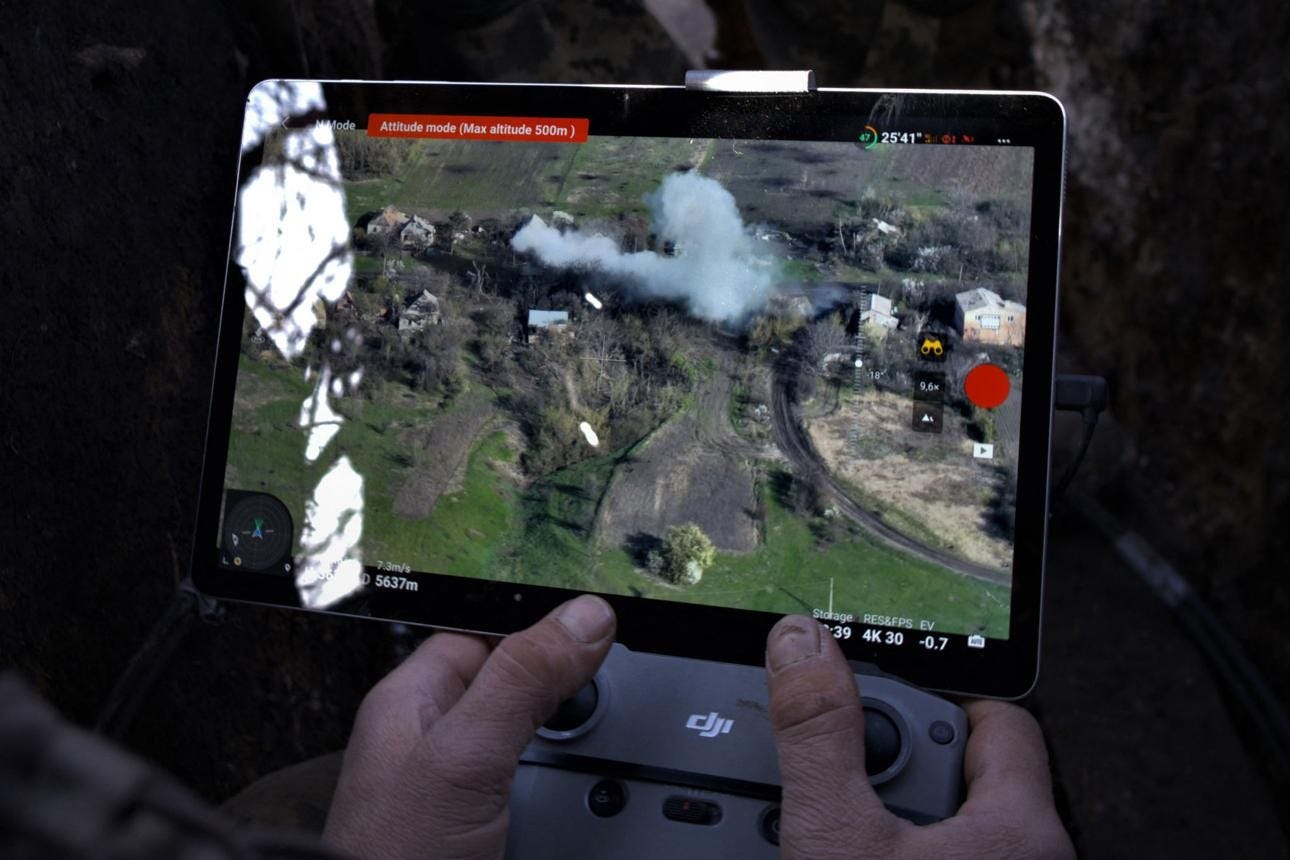
For NATO planners and adversaries alike, the lesson is unmistakable: survivability on the modern battlefield now depends less on armor thickness and more on visibility, signature management, and the ability to operate within a contested, sensor-saturated environment where every movement can be observed and targeted in near real time.
NATO Transformation: From Alliance to System
NATO 2.0
NATO 2.0
Since 2022, NATO has begun evolving from a traditional military alliance into a broader security system designed to operate continuously rather than react episodically.
This transformation is taking place across headquarters in Brussels, national capitals, and forward-deployed commands throughout Europe. It includes deeper integration with the European Union’s defense mechanisms, expanded bilateral agreements among member states, and direct coordination with Ukraine.
The goal is to create a structure that can absorb shocks, maintain operational continuity, and respond at multiple levels simultaneously. This evolution reflects a recognition that the alliance must function not only in times of declared war, but in an environment of constant pressure below that threshold.
NATO: The System They Cannot Break
For Russia, NATO is a strategic problem.
Its strength is not just military. It is intelligence integration. Multiple nations, multiple agencies, fused into a shared operational picture.
Counterintelligence across NATO has evolved significantly. Russian networks are identified faster, disrupted more aggressively, and exposed more publicly.
But NATO’s vulnerability remains political cohesion. That is the seam Russian intelligence will continue to target.
Regional Acceleration: JEF and NB8
In response to the speed of Russian operations, smaller regional groupings have taken on a more prominent role in European defense.
The Joint Expeditionary Force, led by the United Kingdom and composed of Northern European states, has developed into a flexible, high-readiness framework capable of acting quickly without requiring full NATO consensus.
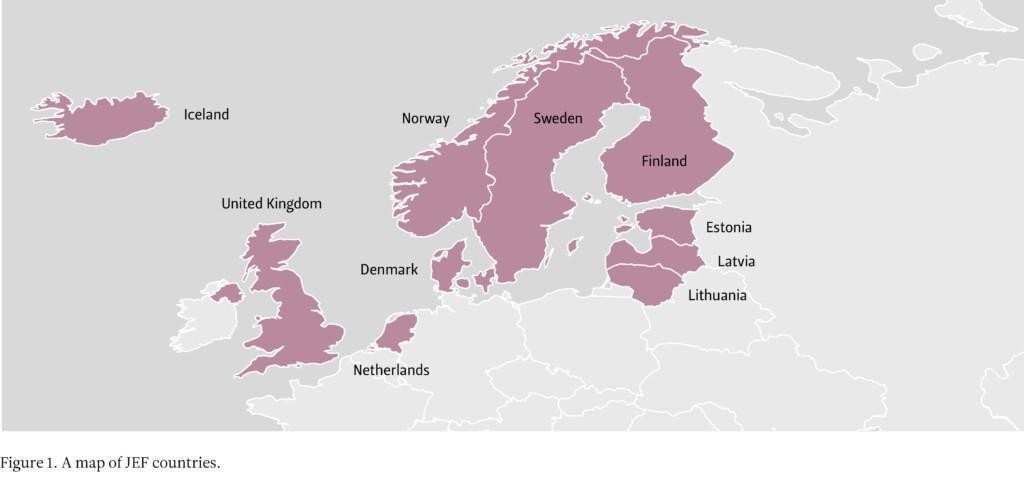
It is a high-readiness coalition designed for rapid deployment across Northern Europe, the Baltic region, and the High North. It brings together ten like-minded nations—United Kingdom, Denmark, Estonia, Finland, Iceland, Latvia, Lithuania, Netherlands, Norway, and Sweden—focused on collective security, rapid crisis response, and deterrence against regional threats, particularly along NATO’s northern and eastern flanks.
Unlike standing NATO forces, the JEF is highly flexible, able to act independently or in support of NATO, emphasizing speed, interoperability, and political cohesion among its members in response to emerging crises, especially those linked to Russian hybrid and conventional military activity.
The Nordic-Baltic Eight (NB8)—Denmark, Estonia, Finland, Iceland, Latvia, Lithuania, Norway, and Sweden—have significantly deepened regional defense integration, expanding cooperation across air defense, naval operations, and intelligence sharing in response to an increasingly contested security environment in Northern Europe.
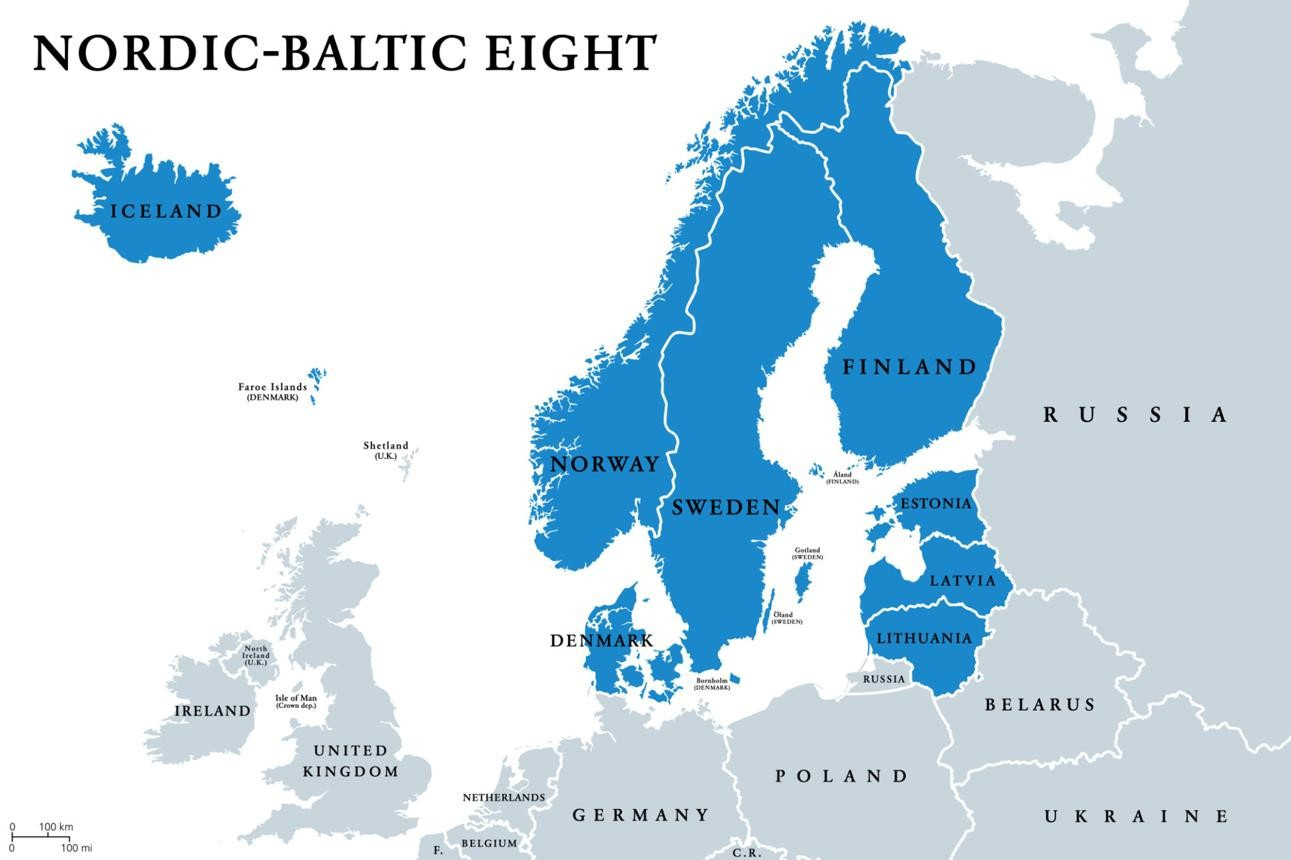
This coordination now includes integrated air policing and early warning systems, joint maritime patrols across the Baltic and North Seas, and near real-time intelligence fusion on Russian military movements and hybrid activities. The effort is designed to compress decision timelines, enhance situational awareness, and create a layered deterrent architecture that complements—and, if necessary, can operate alongside—NATO structures, reflecting a growing recognition among these states that regional self-reliance is becoming a critical hedge against uncertainty in broader alliance dynamics.
These initiatives are rooted in geographic proximity to Russia and a shared understanding of the threat environment. They provide a mechanism for faster decision-making and localized response, complementing NATO’s broader structure while reducing reliance on slower alliance-wide processes.
Intelligence Integration: The Quiet Revolution
Across NATO, intelligence services have undergone a decisive shift from episodic reporting to continuous, networked operations—what practitioners increasingly view as a persistent battlespace rather than a series of discrete crises.
Agencies such as MI6, GCHQ, and their European counterparts are now fused into near real-time intelligence ecosystems, integrating human intelligence (HUMINT), signals intelligence (SIGINT), cyber collection, and open-source intelligence (OSINT) into unified analytic pipelines.
This transformation enables faster attribution of hostile activity, tighter feedback loops between collection and operations, and synchronized responses to hybrid threats ranging from cyber intrusions to influence campaigns.
The result is a quieter but far more consequential revolution: intelligence is no longer a supporting function—it is the operational backbone of deterrence and decision-making across the alliance.
Strategic Shift: Exposure Over Silence
Western governments—particularly across NATO—have moved away from the traditional intelligence norm of quiet handling and deniability, increasingly opting to publicly attribute hostile actions to Russia in near real time.
This shift reflects a deliberate strategy: exposing malign activity—whether cyber intrusions, disinformation campaigns, or covert sabotage—aims to preempt escalation, deny adversaries plausible deniability, and shape global perception before false narratives can take hold.
By declassifying select intelligence and coordinating public statements across allied governments, agencies such as MI6 and GCHQ, alongside European partners, are turning transparency into a tool of deterrence—signaling both capability and resolve while redefining the informational battlespace as a domain where speed, credibility, and narrative dominance are as critical as traditional military power.
Critical Infrastructure: The Primary Battlespace
Across Europe and the North Atlantic, critical infrastructure has become the central arena of competition in what is effectively a persistent, undeclared conflict environment.
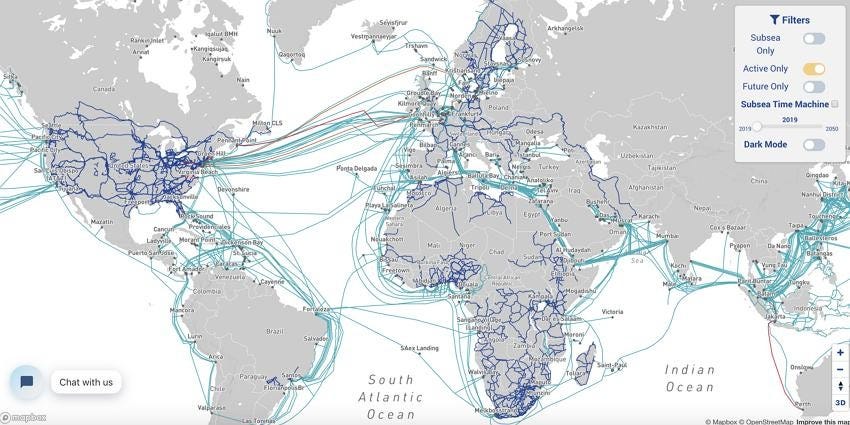
Undersea fiber-optic cables carrying the majority of global communications, energy pipelines supplying fuel across borders, transportation networks moving both commercial goods and military equipment, and the financial systems that underpin economic stability are now routinely monitored, probed, and, in some cases, deliberately disrupted.
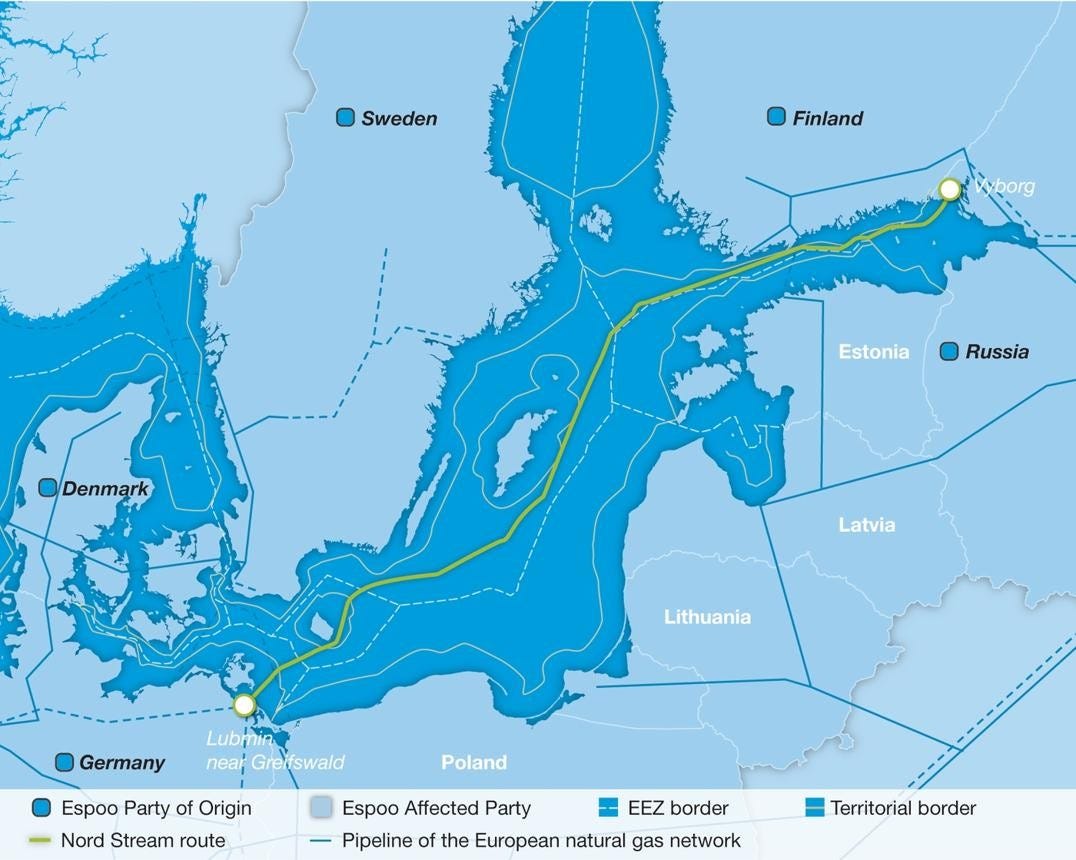
This targeting reflects a strategic logic: rather than confronting NATO militarily, adversaries seek to exploit systemic vulnerabilities—creating friction, uncertainty, and economic pressure below the threshold of open war.
The result is a battlespace where resilience, redundancy, and rapid attribution have become as critical as traditional defense, and where the line between civilian infrastructure and military target has effectively collapsed.
Agents of Influence
Russian operations increasingly extend beyond traditional military and cyber domains into the political and social fabric of Western societies, leveraging influence as a strategic weapon.
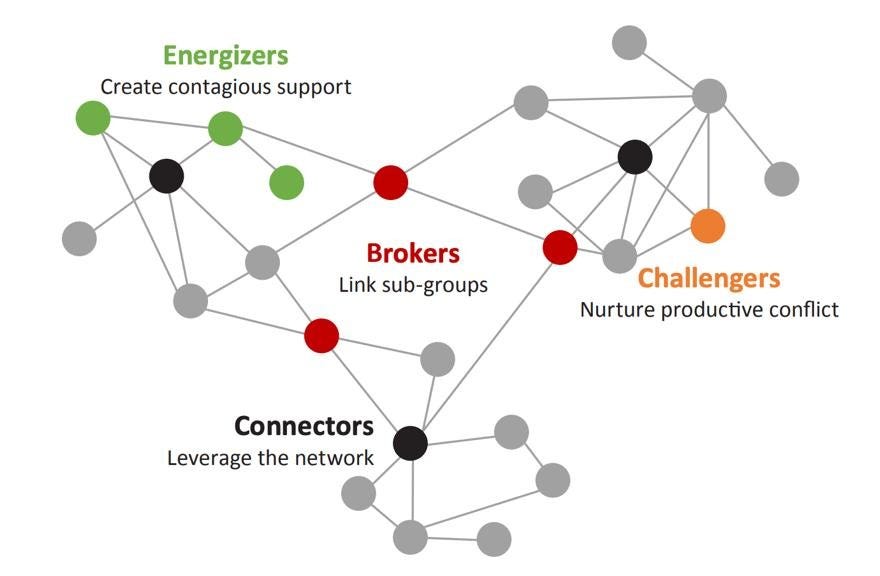
Through intelligence services and affiliated networks, relationships are cultivated with political figures, media organizations, business leaders, and academic institutions—often subtly, sometimes overtly—to shape narratives, distort public discourse, and amplify existing societal divisions.
These efforts are coordinated by entities linked to the Russian Intelligence Services and are designed to operate below the threshold of attribution, exploiting open societies where access, trust, and information flow are strengths but also vulnerabilities. The objective is not necessarily to persuade outright, but to confuse, polarize, and erode confidence in democratic institutions—creating an environment where truth becomes contested terrain and decision-making is degraded from within.
Defense Industrial Capacity: The New Deterrent
The war in Ukraine and the broader security environment have exposed limitations in Western defense production capacity.
European nations, working alongside NATO, have begun accelerating a structural shift toward sustained defense readiness, marked by expanded industrial output, streamlined procurement processes, and the exploration of new financing mechanisms to support long-term military capacity.
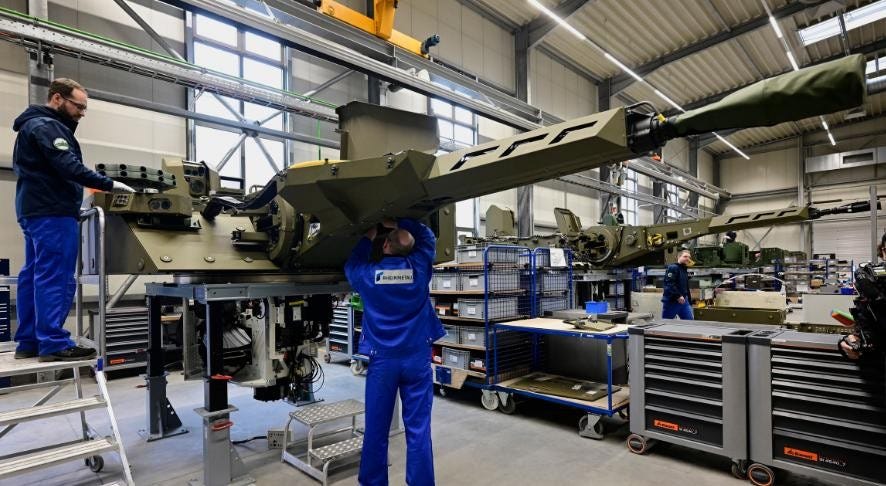
Governments across Europe are reopening or scaling defense production lines for munitions, armored systems, and naval assets, while reforming acquisition frameworks to reduce bureaucratic delay and enable faster fielding of capabilities. At the same time, innovative funding approaches—including joint procurement initiatives, multinational investment pools, and public-private partnerships—are being advanced to ensure durability beyond short-term crisis response.
This effort reflects a growing recognition that deterrence in the current environment is not episodic but continuous, requiring an industrial base capable of supporting prolonged competition and potential conflict.
The Central Risk: Tempo Mismatch
At the core of the current strategic environment is a mismatch in operational tempo. Russian intelligence and military systems operate continuously, executing actions daily across multiple domains.
NATO, by contrast, remains structured around consensus-driven decision-making processes that require alignment among multiple governments.
This creates delays that can be exploited, allowing adversaries to achieve incremental gains without triggering a unified response.
Efforts to accelerate decision-making through regional frameworks and intelligence integration are underway, but the gap remains a defining vulnerability. Managing this imbalance—without sacrificing alliance cohesion—will determine whether NATO can effectively counter sustained hybrid pressure.
Bottom Line
The West is engaged in a long-duration competition that does not resemble traditional war. It is a continuous contest between a centralized system capable of rapid, integrated action and a decentralized alliance built on shared values and collective decision-making.
Russia is testing whether pressure applied over time can fracture that alliance.
NATO is testing whether it can adapt without losing what makes it strong.
The decisive factor will not be a single event. It will be whether the alliance can move fast enough, think clearly enough, and remain unified long enough to withstand the pressure already being applied.
The danger is not collapse in a moment of crisis.
Russian intelligence is a capable and dangerous adversary. It is also constrained by the very system that empowers it.
It is strongest in ambiguity, influence, and long-term positioning. It is weakest when forced into transparency, rapid decision cycles, and environments it does not control.
This is not a contest decided in a single operation. It is a continuous competition between systems.
The one that adapts faster, learns deeper, and sustains its will longer will prevail.