
A National Security Assessment: To Stop Spies, Poke Out Their Eyes
By: Ken Robinson
Strategic Frame
NATO could punish Russia by severing internet, satellite, and financial access. How could the alliance do it lawfully, coherently, proportionately, and without harming itself more than it harms Moscow?
Czech President Petr Pavel has put a blunt idea on the table: Russia has learned to operate below the Article 5 threshold, so NATO should consider asymmetric measures that impose real cost without direct mass casualties.
The proposal itself is strategically significant because Pavel is not a fringe commentator. He is a former Chairman of NATO’s Military Committee and former Czech Chief of Defense, giving his comments unusual operational credibility inside alliance circles.
The Guardian reported that Pavel mentioned disabling Russian internet or satellite access, disconnecting Russian banks from global financial systems, and shooting down unmanned or manned aircraft that violate NATO airspace. The Guardian reported the remarks on May 22, 2026.
Pavel is not proposing a button.
There is no single switch marked Russia.
The proposal is a campaign, not an event.
It would require law, diplomacy, intelligence preparation, cyber operations, private sector coordination, financial controls, maritime and space policy, escalation signaling, and a disciplined public explanation.
Done badly, it becomes a gift to Moscow: proof for domestic propaganda, justification for reprisals, and pressure on Western companies, undersea cables, banks, satellites, and elections.
Done well, it becomes a controlled coercive instrument: reversible, targeted, allied, and tied to observable Russian behavior.
Current State: Fifth Generation War Has Already Begun
Russia, China, Iran, and North Korea are not operating as a formal Warsaw Pact. They are operating as a pressure system. Each brings different tools:
Russian sabotage and influence
Chinese scale, cyber access, industrial depth, and coercive economics
Iranian proxy warfare and illicit finance
North Korean missiles, munitions, cyber theft, and strategic recklessness.
The 2026 Annual Threat Assessment of the U.S. Intelligence Community describes Russian gray zone tools as cyber attacks, disinformation and influence operations, energy market manipulation, military intimidation, and sabotage, often hidden or denied to complicate response.
The same threat environment shows accelerating cooperation among adversarial states.
The 2025 U.S. intelligence assessment warned that growing cooperation among China, Russia, Iran, and North Korea expands risk because hostilities with one can draw in the others. The 2026 ODNI assessment and the 2025 ODNI assessment are the baseline documents for this judgment.
Microsoft’s 2025 Digital Defense Report adds the operational layer: nation-state actors are using cyber and influence operations with more advanced, targeted, scalable tactics, including artificial intelligence-enabled influence activity. Microsoft assessed that state actors rapidly adopted AI for large-scale influence campaigns.
This is the new battlespace: code, finance, satellites, public perception, legal ambiguity, and political exhaustion.
Russia’s method is familiar:
Create pressure
Deny ownership
Watch Western lawyers debate thresholds
Then repeat.
Drones, airspace probes, cyber intrusions, sabotage, assassinations, cutouts, and information operations are not separate lines of effort.
They are one campaign.
The purpose is not always battlefield victory. It is paralysis. Moscow wants NATO governments arguing over attribution while Russian services continue the operation.
What “Shutting the Door” Actually Means
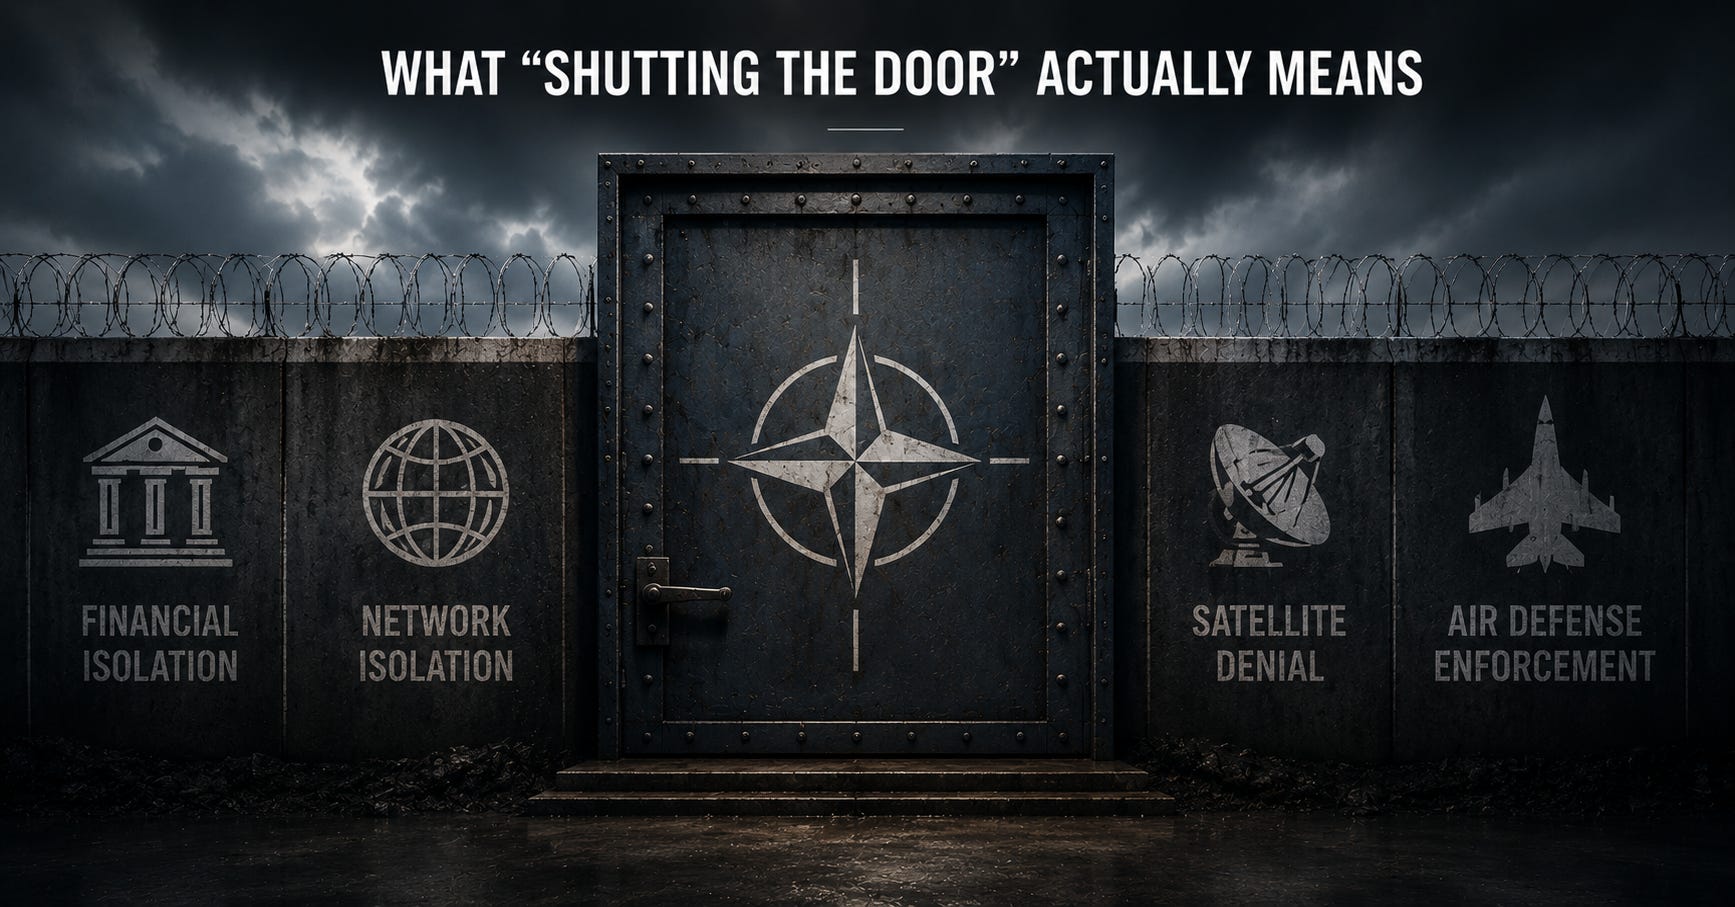
A serious version of Pavel’s proposal has four distinct tracks:
First, financial isolation: expand disconnection of designated Russian banks and payment channels from Society for Worldwide Interbank Financial Telecommunication (SWIFT), correspondent banking, dollar and euro clearing, insurance, reinsurance, and securities settlement.
Second, network isolation: restrict Russian state, military, intelligence, sanctions-evasion, and command-and-control traffic from Western-owned cloud, transit, domain, certificate, hosting, and content distribution services.
Third, satellite and space denial: restrict access to Western commercial satellite services, geolocation, imagery, maritime data, and satellite communications used by Russian forces or sanctioned entities.
Fourth, kinetic air defense enforcement: establish predictable rules for drones and aircraft that violate NATO airspace, including shoot-down authorities after warning criteria are met.
None of those tracks is technically or legally identical:
SWIFT is a Belgian cooperative operating under Belgian and European Union law.
Internet routing is decentralized and privately operated.
Satellite access sits across national regulators, commercial contracts, export controls, spectrum licenses, and military authorities.
Air defense is national and NATO-integrated but still requires rules of engagement, attribution standards, and escalation control.
The phrase “cut Russia off” is rhetorically satisfying.
The practical version is a layered denial architecture.
Mechanics and Procedures
1. Political authorization
The first requirement is an agreed allied trigger. NATO and the European Union would need to define the Russian conduct that activates measures: repeated airspace violations, sabotage on NATO territory, cyber attack against critical infrastructure, attempted assassination, undersea cable interference, major election interference, or direct support to hostile proxy actions. Without a trigger matrix, the alliance will fracture at the first hard decision:
The North Atlantic Council would need to approve the military posture and political message.
The European Union would need sanctions legislation for financial and commercial restrictions. T
The Alliance: United States, United Kingdom, Canada, Japan, Australia, South Korea, Norway, and Switzerland would need parallel controls.
The G7 should become the coordination chamber because it controls much of the relevant finance, export control, insurance, maritime, and technology policy.
2. Legal architecture
A lawful campaign would rely on sanctions statutes, export-control authorities, telecommunications licensing, financial crime authorities, cyber defense authorities, national emergency powers, and military rules of engagement.
It should not be framed as collective punishment of Russian civilians. The cleaner legal theory is targeted denial of capabilities used by the Russian state, intelligence services, military-industrial base, sanctioned banks, proxy networks, and sanctions-evasion infrastructure.
The financial precedent already exists. In 2022, the European Union agreed to exclude key Russian banks from SWIFT, and SWIFT states that, because it is incorporated under Belgian law, it disconnected designated Russian entities when EU regulations required it. European Commission announcement on Russian bank exclusions from SWIFT; SWIFT explanation of sanctions compliance.
3. Intelligence preparation of the environment
Before any major action, allied intelligence services would need a living map of Russian dependencies: banks, front companies, cloud providers, data centers, submarine cable paths, satellite terminals, command-and-control nodes, crypto exchanges, domain registrars, certificate authorities, shipping insurers, payment processors, and telecommunications carriers.
This must include dependencies of Russian military units, intelligence services, sanctions-evasion networks, and war-support industries.
The goal is not to “break the internet.” The goal is to identify which digital and financial dependencies create military and state coercive leverage while minimizing harm to humanitarian communication, civil aviation safety, nuclear risk reduction, medical supply chains, and dissident access to outside information.
4. Private-sector execution
Most of the switchgear is not in government hands. It sits with banks, satellite companies, cloud providers, domain registries, telecom carriers, insurance markets, cable operators, maritime data firms, cybersecurity vendors, and payment systems.
Governments can compel, regulate, indemnify, or coordinate them.
They cannot pretend they own the whole machine.
That means standing up an Allied Technical Denial Cell with cleared representatives from the United States, European Union, United Kingdom, Canada, key Nordic and Baltic states, Japan, Australia, and selected private providers.
Its work would be compartmented but legally supervised. It would build target packages, deconflict humanitarian exceptions, issue compliance guidance, and monitor blowback.
5. Phasing
Phase One should be signaling and hardening: announce a trigger matrix, pre-position sanctions packages, harden allied critical infrastructure, increase cable and satellite monitoring, and warn Russian leadership through public and private channels.
Phase Two should be targeted denial: additional bank removals, export-control tightening, cloud and hosting restrictions for sanctioned entities, satellite service termination for military-linked users, and maritime insurance pressure.
Phase Three should be broader coercive isolation if Russia escalates: wider financial disconnection, domain and hosting restrictions for state platforms, broader technology service denial, and military enforcement against airspace violations.
Phase Four should be restoration: reversible relief tied to verified Russian behavior, ceasefire compliance, withdrawal benchmarks, or cessation of sabotage.
Pros
The strongest argument for Pavel’s proposal is deterrence restoration. Russia has become comfortable with the gray zone because the West often answers with statements after the fact. A coordinated denial campaign would make Russian planners price the next provocation differently. It would also exploit real Russian dependencies.
Moscow has built alternatives, but not full substitutes. Its sovereign internet remains imperfect, its economy still needs external payments, and its military still benefits from commercial satellite, maritime, and technology flows.
There is also a domestic Russian angle.
Russia has been building its own sovereign internet architecture and expanding restrictions against independent information.
The Organization for Security and Cooperation in Europe-linked analyses and reporting by specialist outlets describe a worsening campaign of isolation, throttling, VPN pressure, and preparations for whitelist access models.
OSW reported in March 2026 that Russia had accelerated internet shutdown measures; Freedom House found Russia internet freedom had reached a new low in 2025. Western policy can exploit that contradiction: the Kremlin wants control, but it does not want the economic cost of full isolation.
A disciplined campaign also reassures frontline allies. Baltic, Nordic, Polish, Czech, Romanian, and Black Sea states have lived with Russian pressure for years. They do not need lectures about escalation. They need evidence that the alliance can impose cost below the nuclear threshold.
Cons and Boomerang Risks
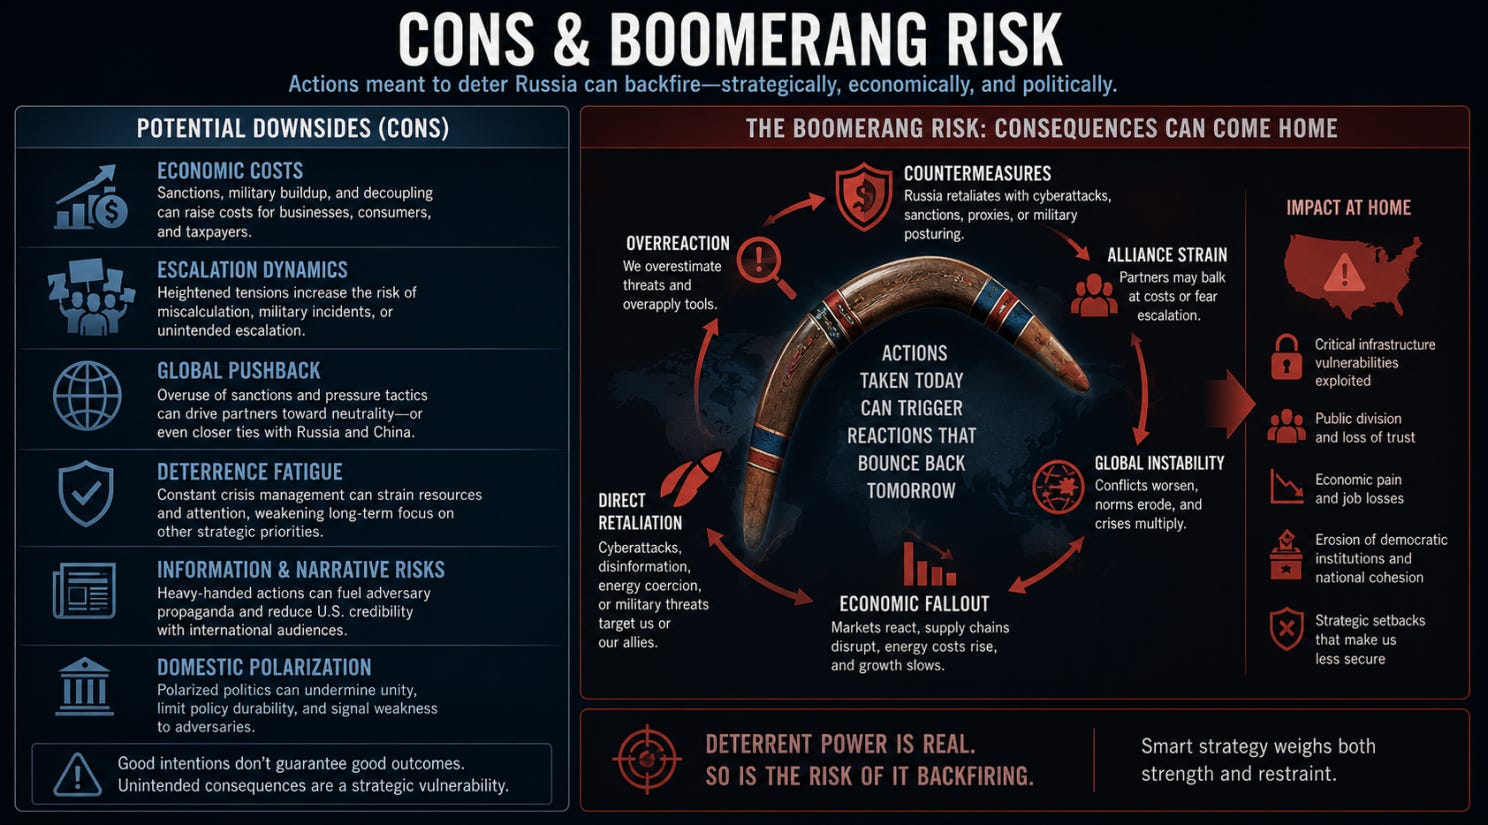
The first boomerang risk is self-harm. Western companies still have exposure to Russian-linked contracts, data, maritime flows, aviation services, commodity payments, and third-country intermediaries. A sloppy shutdown could disrupt global markets, raise energy costs, damage European exporters, complicate humanitarian activity, and create litigation.
The second risk is propaganda. Moscow would portray the campaign as Western war against the Russian people. That message will not persuade everyone, but it will reinforce Kremlin control and help justify further repression. Cutting ordinary Russians off from outside information could serve Putin’s domestic objective unless exceptions and circumvention support are built into the plan.
The third risk is retaliation. Russia is reliable for tit-for-tat, but it often chooses asymmetry rather than symmetry. If NATO pressures Russian connectivity, Russia may not merely pressure Western connectivity. It may attack cables, satellites, pipelines, banks, ports, elections, defense contractors, diaspora communities, or political leaders through cutouts.
The fourth risk is escalation ambiguity. A cyber or satellite denial operation can look like preparation for war. If Russian early warning, nuclear command communications, civil aviation safety systems, or crisis communication channels are affected, escalation risk rises sharply. These areas must be firewalled unless Russia itself crosses a much higher threshold.
Likely Russian Countermoves
Russia’s likely response would be tiered.
Politically, it would accuse NATO of aggression and seek support from China, Iran, North Korea, and parts of the Global South.
Economically, it would accelerate alternative payment systems, use Chinese banks and intermediaries, increase barter and commodity settlement, rely on crypto and stablecoin workarounds, and expand sanctions-evasion networks through the Caucasus, Central Asia, Gulf states, Turkey, and maritime gray markets.
Technically, it would intensify attacks on Western critical infrastructure, pre-position malware, increase ransomware pressure through tolerated criminal groups, and target telecom, cloud, and financial services.
Militarily, Moscow would test NATO airspace, maritime boundaries, and electronic warfare thresholds. It might jam Global Positioning System signals in the Baltic and Black Sea regions, harass reconnaissance aircraft, probe undersea infrastructure, and use drones or deniable sabotage teams.
Politically, it would amplify anti-war, anti-NATO, energy-price, migration, and civil-liberties narratives inside Western societies.
The most dangerous countermove would be a calibrated attack designed to divide the alliance: a cable incident with ambiguous attribution, a cyber attack routed through third countries, a proxy strike against a Western-linked facility, or a banking disruption that Moscow denies while hinting it can do more. Russia’s sweet spot is damage without confession.
Western Countermeasures
The answer is not to avoid action. It is to prepare the battlefield before action.
First, harden critical infrastructure before the first sanction package is announced: banks, energy grids, satellite ground stations, ports, rail systems, undersea cables, cloud providers, water systems, and emergency communications.
Second, pre-brief industry. No Western government should discover private-sector dependencies after the order is signed.
Third, build public attribution capacity. The alliance must be able to explain Russian retaliation quickly, credibly, and with evidence where possible.
Fourth, protect Russian civil society access where feasible. Keep humanitarian communications, dissident circumvention tools, independent media access, family messaging, medical channels, and crisis communications open.
Fifth, create an escalation hotline architecture. The West should be ready to punish Russian behavior while keeping nuclear risk-reduction channels open.
Sixth, pair every coercive action with an off-ramp: stop sabotage, stop airspace violations, stop attacks on critical infrastructure, and specified restrictions can be paused or reversed.
Seventh, build a retaliation ladder before Moscow climbs its own. For every likely Russian countermove, NATO and the G7 should pre-agree a response. Cable sabotage triggers maritime surveillance, sanctions on responsible units, cyber countermeasures, and insurance penalties.
Election interference triggers exposure, expulsions, asset freezes, and platform disruption. Bank cyber attacks trigger coordinated financial defense and retaliatory sanctions against enabling institutions.
The Obama Precedent
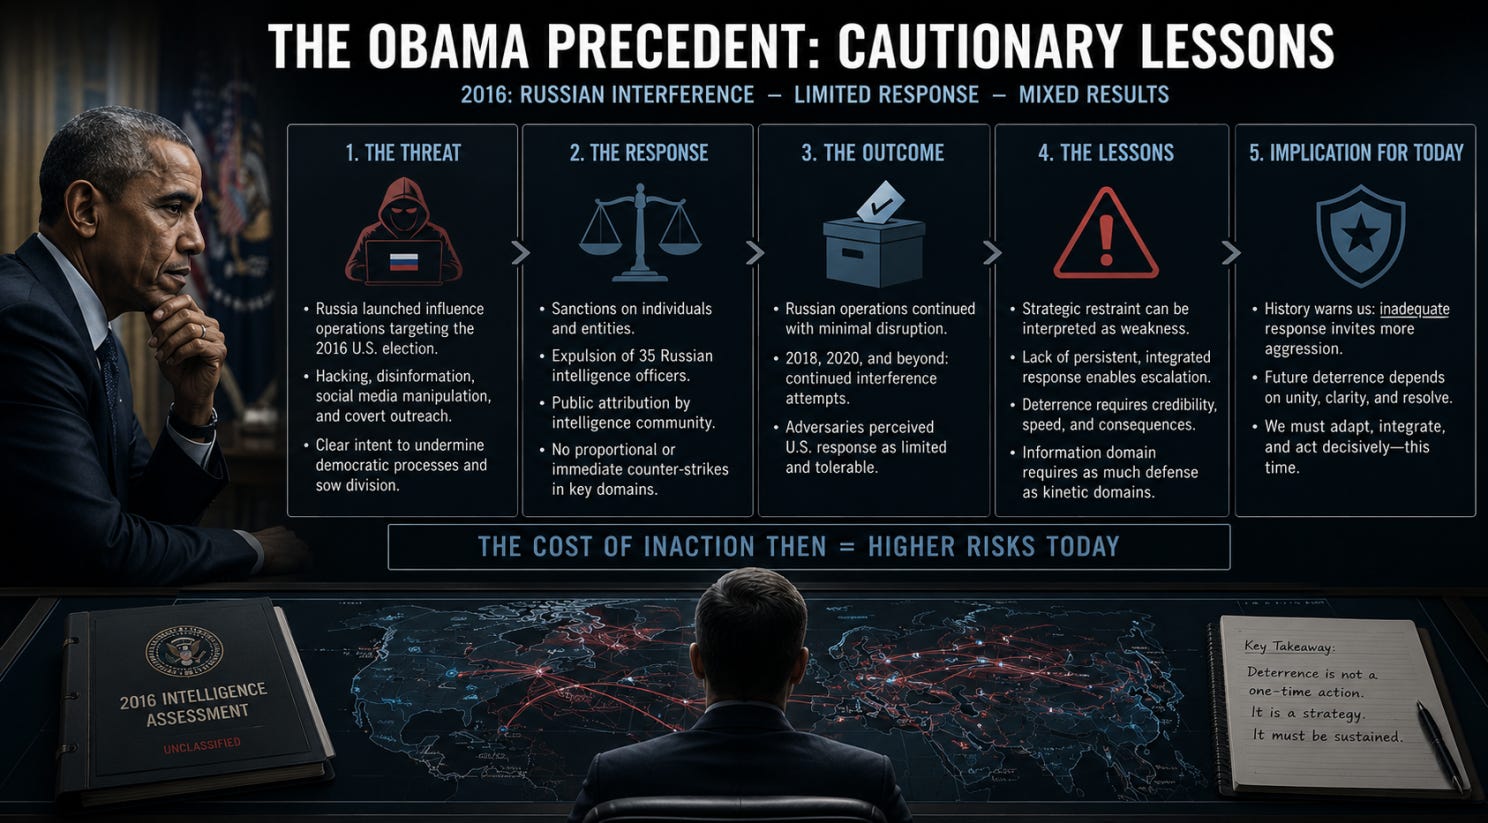
The relevant American precedent is December 2016. President Obama ordered actions against Russia for malicious cyber activity and harassment of U.S. officials, including sanctions and denial of access to Russian compounds in Maryland and New York.
The White House described the actions as a response to Russian cyber operations aimed at the U.S. election and harassment of American personnel. Obama White House statement, December 29, 2016.
The aftermath matters. The incoming administration asked the Russian ambassador to ask Moscow to refrain from escalating in response to U.S. sanctions, to preserve a path to better relations, once Obama left office.
Russia watches U.S. political transitions, alliance fractures, and internal divisions. Any new coercive campaign must be built to survive elections, coalition changes, and disinformation pressure.
Policy Hurdles
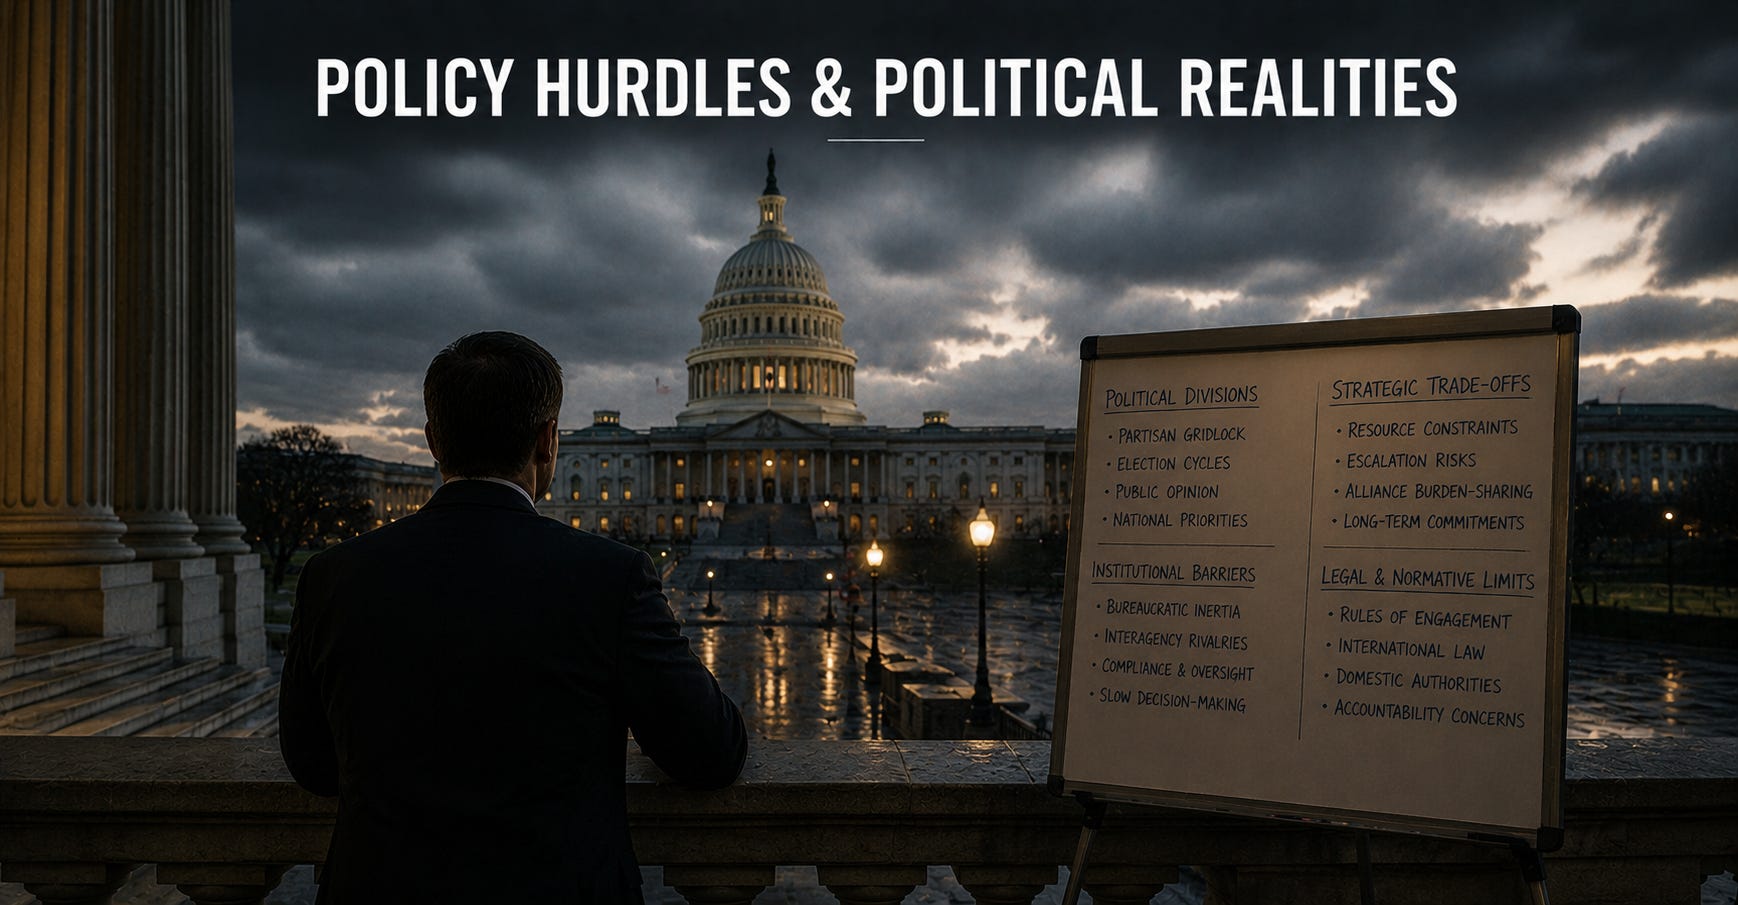
Options
The European Union will be central because of SWIFT, sanctions law, data regulation, and commercial exposure. NATO will be central because of deterrence, air defense, and military signaling. The G7 will be central because of finance, insurance, technology, and export controls.
The United States will be central because of cyber capability, dollar clearing, satellite capacity, intelligence reach, and sanctions leverage. But the United States should not attempt this unilaterally.
Unilateral action would make Washington the story, divide Europe, and give Moscow a propaganda target.
The right frame is allied defense against repeated Russian coercion.
The hardest hurdle is not capability.
It is political will sustained through blowback:
Energy prices may move.
Markets may react.
Russia may retaliate.
China may provide partial relief.
Western civil-liberties groups may object if measures appear to cut off ordinary Russians from information.
Industry will demand clarity and indemnity.
Smaller allies will want assurance that they are not being used as tripwires without protection.
These are not reasons to avoid action. They are reasons to plan like adults.
Recommended Path Forward
Continue to Sit and Take It - Or Deter With Consequences:
Russia Only Responds to Force - Never Diplomacy
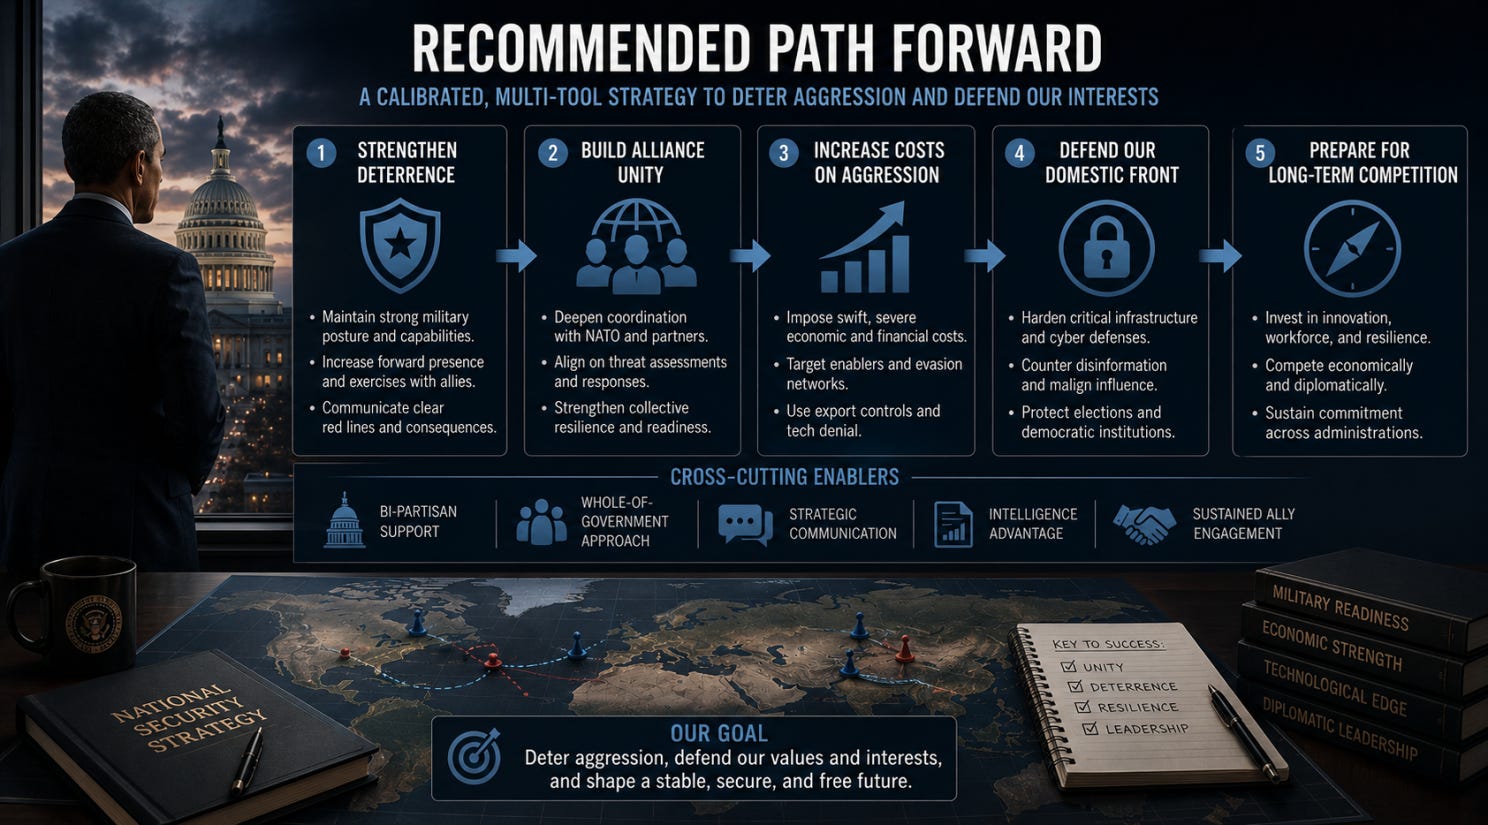
First, create an Allied Russia Coercion Planning Group under a G7 plus NATO-EU umbrella. Its mission should be to draft a trigger matrix, target sets, legal authorities, humanitarian exceptions, private-sector instructions, escalation control procedures, and public messaging.
Second, begin with targeted measures rather than theatrical maximalism. Expand bank and payment restrictions, close sanctions-evasion pathways, terminate commercial satellite and cloud services to sanctioned military-linked users, and prepare airspace enforcement rules.
Third, conduct a private warning to Moscow: continued sabotage, cyber attacks, airspace violations, or attacks on critical infrastructure will trigger specified, reversible denial measures.
Fourth, brief Beijing quietly that material support to Russian workarounds will carry cost.
Fifth, support information access for Russian citizens even while denying Russian state capabilities. The policy should punish the regime and war machine, not help the Kremlin build a prison around its own society.
Sixth, prepare for retaliation before implementation. The West should assume attacks on cables, banks, satellite services, elections, and energy infrastructure.
That assumption should drive readiness, not paralysis.
Bottom Line
To Be, Or Not To Be: Secure
Pavel’s proposal is strategically serious, but only if treated as a campaign of coercive denial rather than a slogan.
Russia has exploited Western fear of escalation by operating below the threshold of open war. The answer is not reckless escalation.
The answer is disciplined escalation management: allied, lawful, phased, reversible, technically precise, and tied to Russian behavior.
The West has the tools. It has demonstrated pieces of them before. What it often lacks is integration and nerve.