
Assessment of Contractor Provenance, Nokia, SORM, and Allied C4I Supply-Chain Risk
Executive thesis
Eduardo Domingues de Jesus has raised a point that NATO, the European Union, and the U.S. defense procurement system cannot casually dismiss: in modern command, control, communications, computers, cyber, intelligence, surveillance, and reconnaissance, the vulnerability is not only the source code, the router, the waveform, the lawful-intercept port, or the cloud pipeline.
The vulnerability is also the human provenance of the people and contractor networks allowed to design, maintain, update, observe, and normalize those systems across both authoritarian and allied environments.
His warning is severe.
But the strategic concern underneath it are very real: when a telecom infrastructure provider has a long history of supporting networks in Russia, including standards-based lawful-intercept interfaces used in the SORM environment, NATO cannot treat that history as irrelevant simply because the vendor is now indispensable to Western defense connectivity.
The key distinction is this: the open record does not prove that Nokia senior executives are Russian agents or that current Nokia Federal personnel are feeding Russian intelligence. It does prove that Nokia, like other major telecom vendors, supplied Russian operators; that Russian networks are subject to SORM interception requirements; that Nokia publicly acknowledged its products included passive lawful-intercept capability required by local law; that the company denied manufacturing, installing, or servicing SORM systems; and that Nokia later stopped deliveries and announced its exit from Russia after the full-scale invasion of Ukraine.
That factual record is enough to justify a hard NATO counterintelligence and supply-chain risk review. It is not enough to justify a public finding of treason, espionage, or executive compromise.
What the evidence supports
The public evidence supports four defensible judgments.
First, Russia’s SORM architecture is not a normal Western lawful-intercept regime with robust independent safeguards. It is a state security access architecture embedded in the telecom environment and historically controlled by the FSB. TechCrunch’s 2019 reporting described leaked Nokia documents concerning lawful-intercept capabilities for Russian telecom providers and summarized SORM as the Russian system enabling security-service access to telecom data. Freedom House has described Russia’s internet environment as sharply deteriorating amid censorship, platform blocking, and state control after the invasion of Ukraine.
Second, Nokia publicly admits that, as a network infrastructure supplier, its products included passive lawful-intercept capability to interface with law-enforcement systems where required by law. Nokia’s position is that this is standards-based, common globally, and not the same as manufacturing, installing, or operating SORM. That distinction matters legally, technically, and ethically. It does not eliminate supply-chain risk; it defines it.
Third, Nokia did business in Russia before the invasion and then stopped deliveries and moved to exit the Russian market after February 2022. Reuters reported in March 2022 that Nokia stopped deliveries to Russia and in April 2022 that Nokia would stop doing business there; Reuters later reported Nokia’s CEO saying the exit would be complete and the company would not deliver anything to Russia. In 2024, Reuters reported that Putin authorized Rostelecom to buy Nokia out of a Russian software joint venture.
Fourth, Nokia Federal Solutions is now an eligible participant in major U.S. defense contracting vehicles, including the Missile Defense Agency SHIELD IDIQ contract with a ceiling of $151 billion. Nokia Federal describes itself as a secure connectivity provider for U.S. federal, defense, civilian, and national security customers. SHIELD is a multiple-award contract vehicle; a seat on it is not the same as a guaranteed $151 billion award, but it does create potential access to sensitive future task orders.
How we got here
The West built its digital nervous system on a commercial assumption that no longer holds. For thirty years, allied governments treated telecommunications as a globalized efficiency market. Vendors built once and sold everywhere. The same core engineering talent, compliance teams, lawful-intercept functions, update channels, maintenance models, and managed-service practices often moved across jurisdictions with radically different rule-of-law environments. That was commercially rational. It was strategically naive.
Russia understood this earlier than we did. Moscow did not need to own every switch if it could compel the legal environment around the switch. Enter SORM.
SORM stands for System for Operative Investigative Activities (Russian: Система оперативно-разыскных мероприятий).
It is a Russian government surveillance framework that requires telecommunications and internet service providers to install equipment that allows Russian security services—primarily the Federal Security Service (FSB)—to monitor communications and internet traffic.
What SORM Actually Does
SORM is not a single device. It is a legal, technical, and regulatory architecture that gives the state access to communications networks.
SORM converted commercial telecommunications into a state-access layer. The Yarovaya-era expansion of Russian surveillance obligations deepened that state demand for data retention and state access. Even when a Western vendor merely provides standards-based interfaces, the operational reality is that an authoritarian state can turn “lawful intercept” into regime security infrastructure.
The West then made a second mistake. After Huawei and ZTE became the public face of 5G security risk, Western procurement institutions shifted toward trusted Western or allied vendors. That was necessary but incomplete.
The question became:
Is the company headquartered in an allied country?
Is the equipment technically certified?
Is the software scanned?
Are the contracts compliant?
Those are important questions. They are not sufficient questions. NATO also has to ask: What foreign sovereign mandates shaped the vendor’s architecture? Which personnel supported authoritarian deployments? Which maintenance relationships persisted? Which subcontractors, former employees, resellers, field engineers, managed-service teams, and integration partners have knowledge of allied configurations? Which people have moved from Russian-market work into allied defense support?
The core risk: not “Nokia is Russia,” but “NATO is exposed”
The strategic danger is not that every Nokia product is suspect or that NATO should blindly exclude a critical Western telecom supplier. That would be operationally reckless. Nokia is one of the few companies with the scale, radio access, transport, optical, fixed-network, private wireless, and Bell Labs depth that the West may need precisely because the Huawei alternative is unacceptable.
The danger is that NATO may be treating vendor nationality and product certification as substitutes for counterintelligence-grade provenance.
A hostile intelligence service does not need a dramatic backdoor if it can exploit maintenance visibility, release timing, configuration drift, update telemetry, integration dependencies, field-support tickets, vulnerability disclosures, lawful-intercept design assumptions, export-control workarounds, or the professional networks of people who once built systems under Russian legal mandates.
The most valuable intelligence may not be the contents of NATO communications. It may be the map of the architecture: what is being modernized, where redundancy is thin, what latency problems remain, which nodes matter, which patches are delayed, which vendors hold privileged access, and which future capabilities are entering test and evaluation.
That kind of information can be turned into Russian countermeasures. It can support electronic warfare planning, cyber targeting, deception, denial, supply interdiction, kinetic target development, and doctrine. In war, metadata about the nervous system can be as useful as the messages moving across it.
Assessment of Eduardo Domingues de Jesus’s warning
The author is right to insist that NATO must audit people, not only products. He is right that “clean slate” corporate restructuring can be meaningless if legacy executives, program managers, architects, subcontractors, and field-support chains retain effective influence over successor personnel. He is right that a company can be technically valuable and still represent a governance and provenance risk. He is right that the risk is not merely moral; it is operational and financial. A defense customer that cannot trust the provenance of a contractor’s privileged human layer is buying future disruption.
But the public record requires discipline. The evidence supports elevated risk. NATO should therefore treat the issue as a counterintelligence problem. The remedy is not accusation first. The remedy is access control, compartmentation, independent verification, contractual leverage, and continuous monitoring.
CYBER BEACON NATIONAL EXERCISES
While a serving Director, National Defense University Foundation, Board of Directors, I delivered opening remarks at CYBER BEACON, addressing continuity of operations in cyberspace and the need to anticipate both natural and malicious disruptions.
I emphasized the following concepts for cyber leadership:
The “Two Halves” of Cyber Risk: I noted that 50% of cyberspace problems are internal, self-inflicted issues driven by poor standards and weak capability maturity models. I urged all national leaders to focus on solving those while preparing to defend against the remaining external threats.
Evaluating Continuity: I connected the disruption caused by natural disasters to cyberspace, challenging leaders to ask tough questions about how organizations will communicate and operate if large populations are denied internet access for extended periods.
Event Recognition: I highlighted that in crisis scenarios, leadership must be able to identify “who did it, and who paid for it” to hold adversaries accountable.
Information Over Preamble: I emphatically stressed the need for action plans over broad policies, operating holistically to solve what can be solved and anticipating what cannot.
Recommendations: What NATO should do now
1. Create a NATO Contractor Provenance Review Board. NATO should stand up a standing board under allied counterintelligence, cyber, acquisition, and legal authorities to review high-consequence vendors in C4I, cloud, telecom, space, missile defense, and critical infrastructure. This board should evaluate not only ownership, beneficial control, and source code, but also executive history, country-of-operation exposure, lawful-intercept obligations, subcontractor chains, privileged-administrator populations, support geographies, and employee movement from authoritarian deployments into NATO-sensitive programs.
2. Impose a “no unilateral inheritance” rule for legacy support teams. No vendor should be permitted to self-certify that a reshuffle created a clean slate. NATO-sensitive task orders should require a customer-approved personnel baseline, including named key personnel, cleared alternates, subcontractor identities, support locations, privileged-access rosters, and a record of prior work in Russia, Belarus, China, Iran, or other high-risk jurisdictions. Personnel substitutions should require government approval, not vendor convenience.
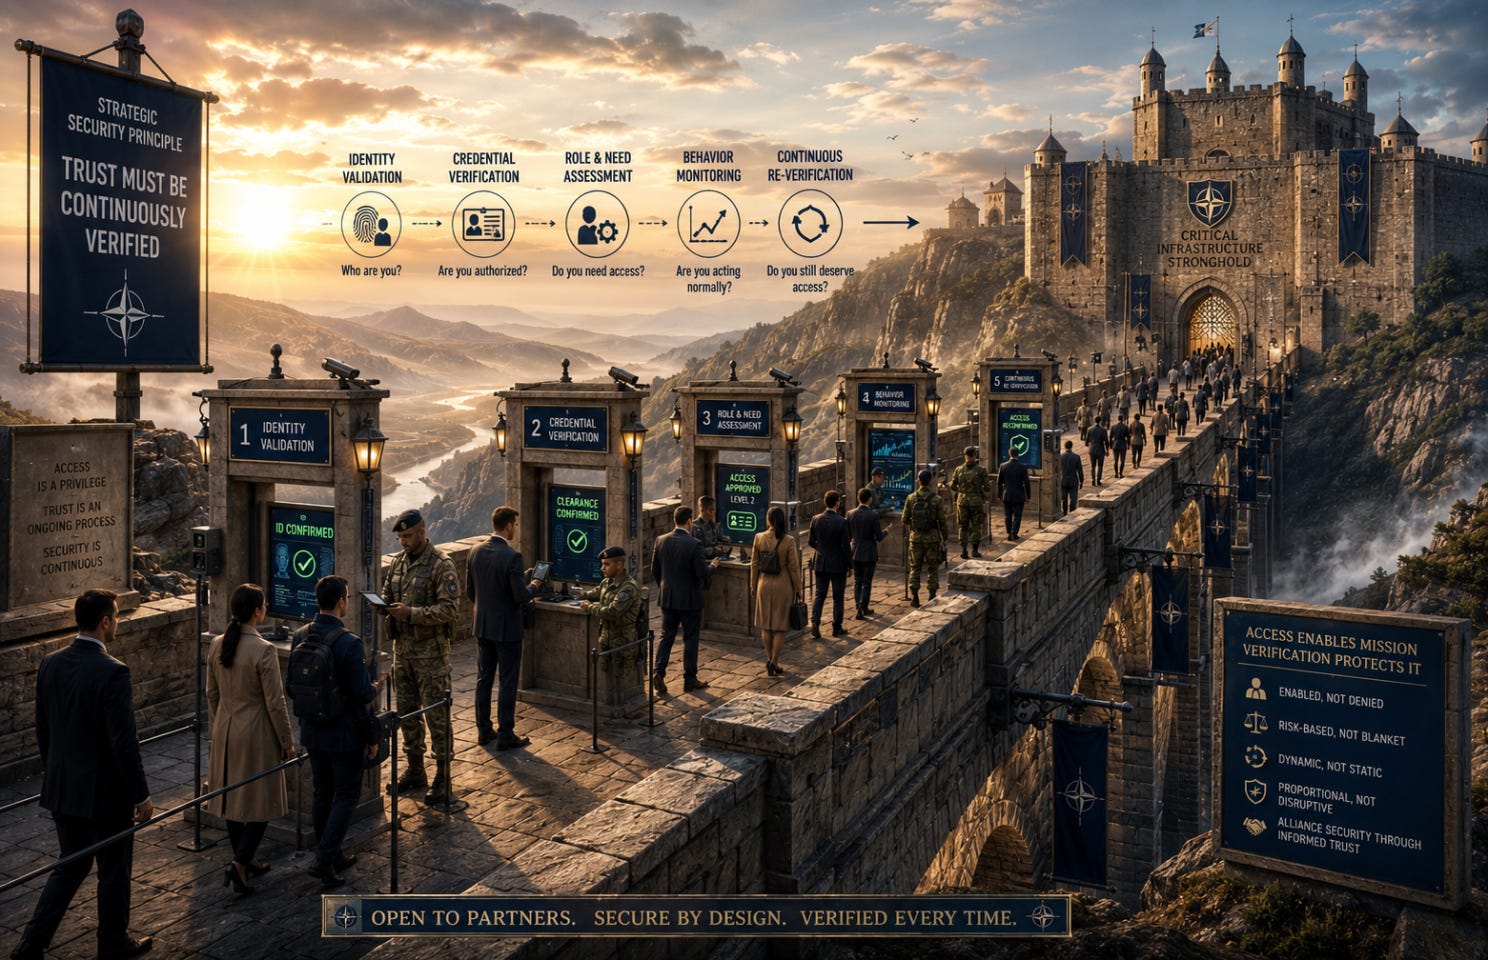
3. Separate technology acceptance from human access. NATO can use Nokia technology where technically necessary while sharply limiting who may see classified architectures, deployment diagrams, configuration files, keys, telemetry, vulnerability data, incident reports, and operational performance data. The product may pass. The person may not. The team may pass. The subcontractor may not. Access must be granular, revocable, logged, and mission-justified.
4. Build sovereign “red-team maintainers.” NATO should create allied maintenance and integration cells capable of independently operating, patching, testing, and validating critical telecom infrastructure without relying exclusively on the original vendor’s field teams. This does not mean nationalizing the technology. It means denying any contractor a monopoly on operational knowledge.
5. Require C-SCRM at the boardroom and task-order level. NIST SP 800-161 Rev. 1 provides a mature model for cybersecurity supply-chain risk management across organizational levels, and CISA emphasizes supply-chain risk management as part of critical infrastructure resilience. NATO should adapt these concepts into enforceable contract clauses: continuous supplier-risk assessment, fourth-party visibility, incident notification, foreign-government pressure disclosure, software bill of materials, hardware bill of materials, secure update provenance, and supplier insider-threat reporting.
6. Treat lawful-intercept history as a special risk indicator. A vendor’s compliance with Russian lawful-intercept rules may have been legal at the time. That does not make it strategically irrelevant now. NATO should require disclosure of products, teams, interfaces, documentation, and support services associated with SORM or equivalent authoritarian lawful-intercept regimes. The purpose is not punishment. The purpose is compartmentation and assurance.
7. Establish allied escrow and reproducible-build requirements for critical components. Where feasible, NATO should require independent source escrow, build verification, firmware provenance, update-signing control, vulnerability disclosure timelines, and the ability to rebuild or replace critical components in crisis. If a vendor cannot support such assurance for national-security systems, the task order should be narrowed until it can.
8. Use zero-trust contractor access. Every vendor access session should be treated as hostile until authenticated, authorized, recorded, and behaviorally validated. No persistent privileged access. No unsupervised remote maintenance into sensitive enclaves. No shared administrator accounts. No unmanaged laptops. No opaque telemetry channels. No vendor-controlled logs as the sole audit source.
9. Conduct a NATO-wide exposure map. The alliance should map where Nokia and all similar vendors sit across NATO networks, EU critical infrastructure, national defense ministries, missile defense programs, transport networks, cloud backbones, military mobility systems, energy grids, and emergency communications. The first question is not “Are they bad?” The first question is “Where are they, what can they see, and what would break if access were denied tomorrow?”
10. Create a trusted allied replacement and diversification plan. The West cannot solve this problem by pretending it has unlimited vendors. It does not. Therefore, NATO should fund diversified allied telecom capacity, open interfaces, interoperable private 5G/6G architectures, sovereign integration capability, and rapid reconstitution pathways. Dependence is manageable only when exit is possible.
Bottom line
Eduardo Domingues de Jesus is pointing at the right battlefield: the human layer of critical technology. His warning should not be dismissed because some of its language is sharper than the public evidence. The strategic issue is bigger than Nokia. It is the entire Western habit of auditing machines while trusting the corporate networks that deliver, patch, observe, and explain those machines.
NATO should not panic. It should not smear. It should not cripple a key Western technology supplier without evidence. But it also cannot continue to confuse commercial compliance with wartime trust. In a European war shaped by drones, EW, cyber effects, targeting networks, satellite communications, and missile defense, the contractor who can see the architecture can help an adversary understand the architecture.
That is not a procurement footnote. That is a counterintelligence problem at alliance scale.
The recommendation is therefore simple: protect the technology where it is necessary, quarantine the human risk where it is unproven, verify every privileged path, and build sovereign allied capacity so no contractor can ever again become too essential to question.
Selected sources
Nokia, “Statement on NY Times,” March 28, 2022: Nokia denial that it manufactured, installed, or serviced SORM equipment; acknowledgment of passive lawful-intercept capability required by law.
TechCrunch, “Documents reveal how Russia wiretaps phone companies,” September 18, 2019: reporting on leaked Nokia documents, lawful-intercept capabilities, and SORM context.
Reuters, “Nokia stops deliveries to Russia,” March 1, 2022; “Nokia to stop doing business in Russia,” April 12, 2022; and December 2022 reporting on Nokia/Ericsson exits.
Reuters, “Russia’s Putin gives Rostelecom approval to buy Nokia out of joint venture,” May 29, 2024.
Nokia Federal Solutions, “Nokia Federal Solutions awarded SHIELD IDIQ contract by U.S. Missile Defense Agency,” March 3, 2026.
NIST SP 800-161 Rev. 1, “Cybersecurity Supply Chain Risk Management Practices for Systems and Organizations,” final publication page.
CISA, “Information and Communications Technology Supply Chain Risk Management,” supply-chain security guidance.
NATO CCDCOE, “National Approaches to the Supply Chain Cybersecurity: Taking a More Restrictive Stance Against High-Risk Vendors,” 2023.
NATO, “Deterrence and defence,” current NATO statement on resilience, critical infrastructure, and supply chains.
Freedom House, “Russia: Freedom on the Net 2023,” reporting on Russia’s deteriorating internet-freedom environment.